Install and Configure WireGuard
From: https://www.stavros.io/posts/how-to-configure-wireguard/
Note: for the client configuration to work you must first have a working wireguard server.
#become root
sudo -i

#install wireguard
apt install wireguard

#create keys
cd /etc/wireguard
umask 077  # This makes sure credentials don't leak in a race condition.
wg genkey | tee privatekey | wg pubkey > publickey
#edit the config
nano -w wg0.conf
Client (Example config file) – wg0.conf
Add the client private key, the server public key, and the server IP address.
[Interface]
Address = 10.5.5.25
PrivateKey = client private key

#-------------DNS
#DNS = 10.5.5.1 #Server caching dnsmasq that forwards to azure in my case
#DNS = 168.63.129.16 #Azure
#DNS = 1.1.1.1 #Cloudflare
DNS = 176.103.130.130, 176.103.130.131 #AdGuard

#-------------MTU
MTU = 1280 #This may need to be changed depending on your connection to the internet.
#MTU = 1384
MTU = 1360

#-------------MSS Clamping
#PostUp = iptables -A FORWARD -p tcp --tcp-flags SYN,RST SYN -j TCPMSS --clamp-mss-to-pmtu
#PostDown = iptables -D FORWARD -p tcp --tcp-flags SYN,RST SYN -j TCPMSS --clamp-mss-to-pmtu


[Peer]
PublicKey = server public key
Endpoint = server IP address:51820
#AllowedIPs = 0.0.0.0/0 #Use this if you want all your traffic to pass through the VPN
AllowedIPs = 10.5.5.25/32

# This is for if you're behind a NAT and
# want the connection to be kept alive.
PersistentKeepalive = 25
Server (Example config file) – wg0.conf
Add the server private key, and each client’s public key.
[Interface]
Address = 10.5.5.1
PrivateKey =
ListenPort = 51820

[Peer]
PublicKey =
AllowedIPs = 10.5.5.5/32

[Peer]
PublicKey =
AllowedIPs = 10.5.5.25/32
Securing
After you’re done, run the following to make the directory and files readable only by administrators (it does contain secret keys, after all):
exit # exit rootsudo chown -R root:root /etc/wireguard/
sudo chmod -R og-rwx /etc/wireguard/*
Start and test wireguard
On both server, and client run:
sudo wg-quick up wg0; wg
#to bring it down
sudo wg-quick down wg0
Automatically run at startup
After you’ve created and secured the file, you can easily set WireGuard to initialize the VPN on startup if your OS is using systemd:
sudo systemctl enable [email protected]
Similarly, to start or stop the service:
sudo systemctl start [email protected]
sudo systemctl stop [email protected]
Android or iOS client
To turn your conf file into a qr code use:
qrencode -t ansiutf8 < wg0.confSet up DNS on the server
From: https://askubuntu.com/questions/1032450/how-to-add-dnsmasq-and-keep-systemd-resolved-18-04
Install openresolv on client
apt install openresolvInstall dnsmasq on server
apt install dnsmasq
nano -w /etc/dnsmasq.conf
server=168.63.129.16 #Azure
#server=176.103.130.130, 176.103.130.131 #Adguard
interface=lo
listen-address=10.5.5.1
bind-interfacesMake DNSMasq start after our wg-quick service:
systemctl edit dnsmasqpaste
[Unit]
[email protected]
[email protected]
Firewall on server
Allow udp port 51820 through your firewall in whatever cloud service you are using.
Allow Wireguard and DNS through local ufw firewall
ufw allow proto udp from any to any port 51820
ufw allow proto tcp from any to any port 53
From: https://ubuntu.com/server/docs/security-firewall
Make sure to edit the firewall policy’s in your cloud server’s management dashboard as well to allow port 52820. In my case, Azure.
sudo ufw status
Status: active

To                         Action      From
--                         ------      ----
22                         ALLOW       Anywhere
51820                      ALLOW       Anywhere
53                         ALLOW       Anywhere
/etc/default/ufw change the DEFAULT_FORWARD_POLICY to “ACCEPT”:
DEFAULT_FORWARD_POLICY="ACCEPT"
Then edit /etc/ufw/sysctl.conf and uncomment:
net/ipv4/ip_forward=1
Now add rules to the /etc/ufw/before.rules file. The default rules only configure the filter table, and to enable masquerading the nat table will need to be configured. Add the following to the top of the file just after the header comments:
# nat Table rules
*nat
:POSTROUTING ACCEPT [0:0]

# Forward traffic from eth1 through eth0.
-A POSTROUTING -s 10.5.5.0/24 -o eth0 -j MASQUERADE

# don't delete the 'COMMIT' line or these nat table rules won't be processed
COMMIT
sudo service ufw restartTest what is my ip, and dns leak
Gnome shell Indicator extension: https://extensions.gnome.org/extension/3160/wireguard-indicator/
Add a quicklaunch shortcut: https://blog.linuxserver.io/2019/11/24/connect-an-ubuntu-client-to-opnsense-wireguard-tunnel-with-a-gui-toggle-in-gnome/
]]>Open Terminal from dash:
sudo apt install dl-youtube
dl-youtube YOUTUBE-URL #Copy and paste from your browser
sudo snap install shotcut --classic
shotcut &Shotcut Manual:
http://write.flossmanuals.net/introduction-to-video-editing-with-shotcut/about-this-guide/
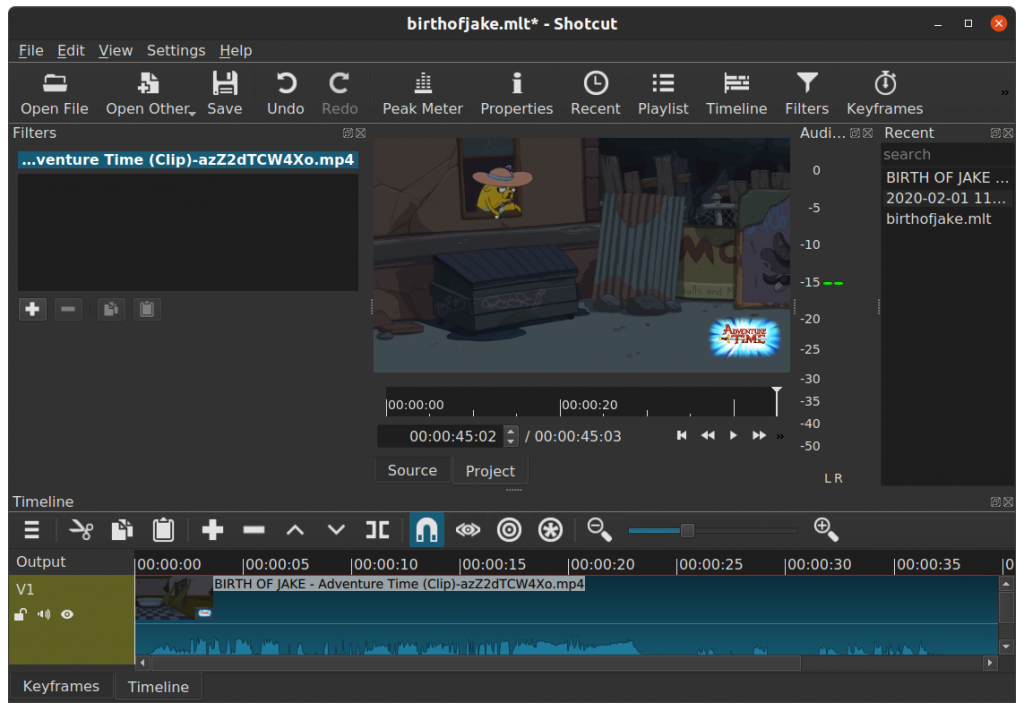
dl-youtube supports many other sites. Visit list here:
https://ytdl-org.github.io/youtube-dl/supportedsites.html

Inspired by this portable secure gateway, I set up my own secure cloud gateway.
Using these three services, Wireguard VPN, Adguard Home, and Tor Anonymizing Proxy. Although TOR doesn’t recommend using TOR in conjunction with VPN’s or proxies, I like this setup the best. For this to work you need a router that can support Wireguard. I use a Netgear r6220 with the Linux based open source router OS, Openwrt. You can easily use any computer that runs Ubuntu instead.
The router I used: https://openwrt.org/toh/netgear/netgear_r6220
Configure your local router
Flash OpenWRT
Set Password
Set LAN subnet
Set Static DHCP lease for desktop
Set name and password for both Wifi Networks
Set Adguard DNS: 176.103.130.130, 176.103.130.131 on wan interface.
Update software lists..
Install nano, curl, ca-bundle, wireguard, etc..
opkg update
opkg install nano curl ca-bundle luci-app-wireguard
reboot
Wireguard
Set up Wireguard on your router with the below guide:
https://www.azirevpn.com/support/guides/router/openwrt/wireguard
Ignore the AzireVPN specific parts.
Time
From: https://forum.openwrt.org/t/initiate-wireguard-after-ntp-success/14751/52
A the end of the guide it says you have to sync the time with the browser after every reboot, because the router does not have a real time clock (RTC). Wireguard needs the time to connect to the other endpoint. However, I found that if you leave the OpenWRT time in UTC, then it shouldn’t need you to do that.
MTU
After making all these changes my upload speeds were terribly slow. To fix this I had to change the MTU of Wireguard interface to 1360. Stop the interface before changing the MTU I think Maybe because I use AT&T 4G which I think has a MTU of 1420.
QOS (SQM – Smart Queue management)
From: https://openwrt.org/docs/guide-user/network/traffic-shaping/sqm
Even if you have nice low latency, low jitter, and high bandwitch up and down you can still experience slow internet. Especially if you do any uploading. Some people call this “buffer bloat”. SQM can mitigate that by managing your traffic to not saturate your upload or download.
You can test your buffer bloat here: http://www.dslreports.com/speedtest
opkg update && opkg install luci-app-sqm
reboot
Play with Download and Upload values until you get good speeds with no buffer bloat.
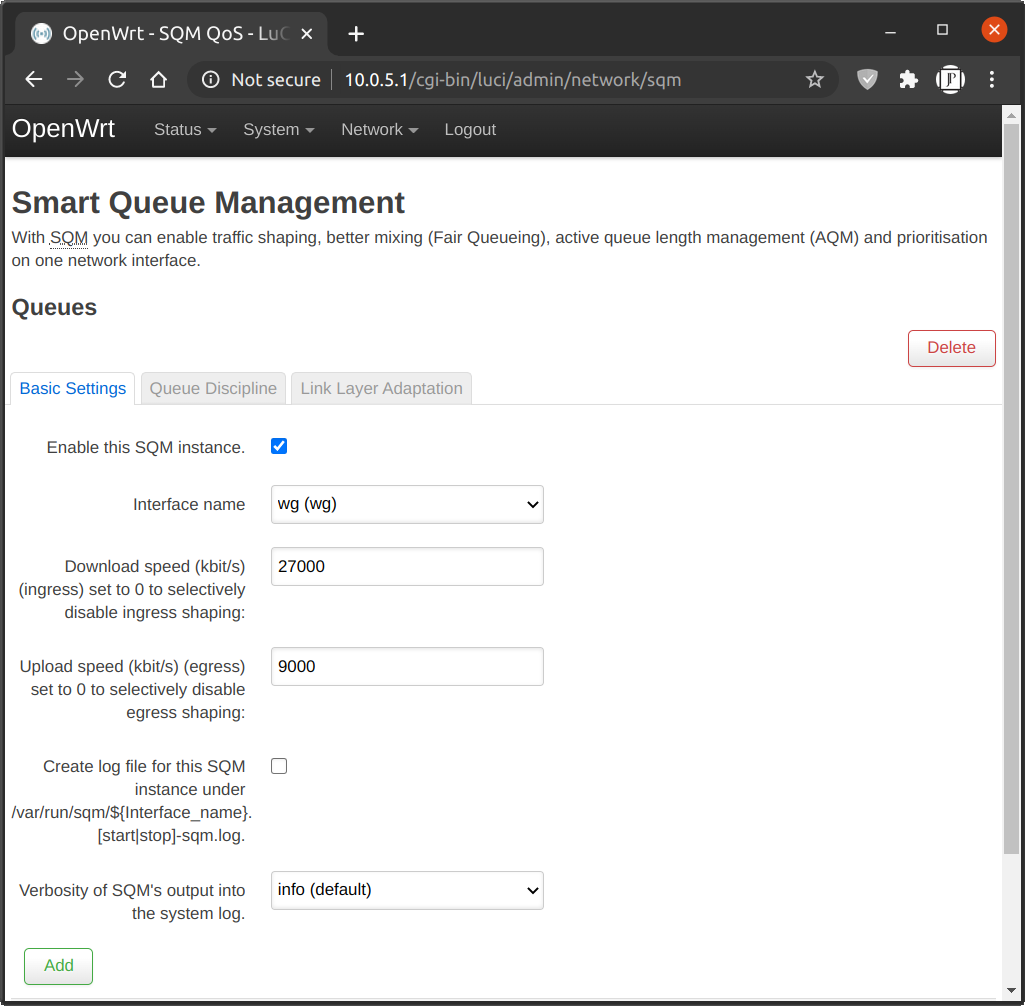
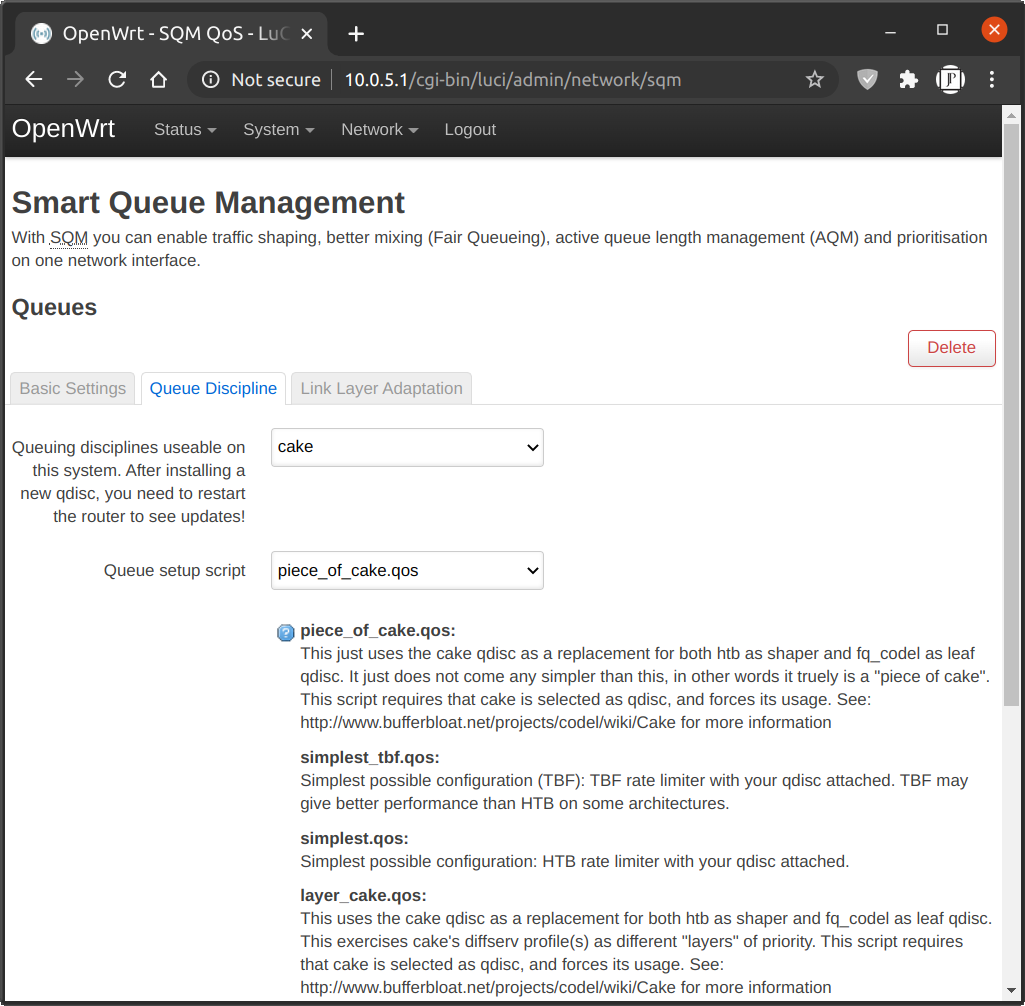
Configure your cloud server
I used Ubuntu 20.04 for my cloud server.
Follow the above guide.

Results: Over VPN with SQM.
The below needs more testing and fleshing out…
AdGuardHome (Optional)
Just using the AdGuard DNS is sufficient for most people, but if you’d like more control over your block lists, you can also install Adguard Home to either the Router, or the cloud gateway.
Gateway: For the gateway it can be done by using the below instructions, but I didnt have luck with the snap. This should let you configure the DNS lists locally.
https://github.com/AdguardTeam/AdGuardHome/wiki/Getting-Started#installation
sudo snap install adguard-home
Or,
Router: https://forum.openwrt.org/t/howto-running-adguard-home-on-openwrt/51678
Adding Tor to the Cloud gateway, or the local router.
To be continued…
https://trac.torproject.org/projects/tor/wiki/doc/TransparentProxy
https://www.linuxuprising.com/2018/10/how-to-install-and-use-tor-as-proxy-in.html
]]>For the backgrounds to work you;ll need a solid color background. I ordered this green screen: https://amzn.to/2ZhoAkK.
I use Google meets, but this should work with any video conferencing software. (Google meets should be rolling out virtual backgrounds, and blurring in the coming months.) From: https://cloud.google.com/blog/products/g-suite/introducing-some-new-meet-features
Install OBS
sudo snap install obs-studioInstall V4L2
sudo apt install v4l2loopback-dkmsCreate dummy video device, and make is persist across reboots.
create the config file:
nano -w /etc/modules-load.d/obscam.confAdd the below contents:
v4l2loopback devices=1 video_nr=10 card_label="OBS Cam" exclusive_caps=1Next time you reboot the module should be automatically loaded. Manually add the module with the currently running system:
sudo modprobe v4l2loopback devices=1 video_nr=10 card_label="OBS Cam" exclusive_caps=1OBS Plugin obs-v4l2sink
NOTE: This step is no longer necessary in modern version of OBS. As it is now a base feature. You may need to restart OBS to see the new “Start Virtual Cam” button to appear.
You may have to install libobs, and libobs-dev
sudo apt install libobs libobs-devDownload and Compile OBS plugin obs-v4l2sink
sudo apt install qtbase5-dev
git clone --recursive https://github.com/obsproject/obs-studio.git
git clone https://github.com/CatxFish/obs-v4l2sink.git
cd obs-v4l2sink
mkdir build && cd build
cmake -DLIBOBS_INCLUDE_DIR="../../obs-studio/libobs" -DCMAKE_INSTALL_PREFIX=/usr ..
make -j4
sudo make install
Now start OBS Studio and configure the V4L2 video output to /dev/video10 via the new menu item “Tools”->”V4L2 Video Output”:

Add a Chromakey filter.
Here is a good guide: https://gamingcareers.com/guides/green-screen-in-obs-slobs/
Add border, presets, LUTs, transitions, etc…
Add scenes like thank you, thumbs up, screen sharing, other camera angles etc…
Using Google Meet with the Virtual Camera
Start a Google Meet via https://meet.google.com/ and go to settings:

More Reading
Pretty cool virtual background way from scratch: https://elder.dev/posts/open-source-virtual-background/
Another cool virtual background: https://github.com/floe/deepbacksub
I’m also testing Webcamoid: https://webcamoid.github.io/. (Seems to crash quite a bit.)
]]>Luckily securing RDP with WireGuard is pretty easy. Plus there is a WireGuard app for most platforms. Windows, MacOS, Linux, iOS, Android, etc.. https://www.wireguard.com/install/
From: https://www.henrychang.ca/how-to-setup-wireguard-vpn-server-on-windows/
Setup firewall rules (just as you would for a Linux server setup: open and forward ports 51820, configure ddns etc)
You can use the handy graphical tool for setting up the VPN with Wireguard for Windows. Simply download, and install the Windows version, and run Wireguard.
From: https://golb.hplar.ch/2019/07/wireguard-windows.html
One feature I like is that the Windows version of WireGuard remembers the VPN connection state. When you reboot Windows while WireGuard is connected to the server, the software automatically reconnects and re-establishes the VPN tunnel when it starts up. This prevents you from accidentally connecting without a VPN.
My server conf
[Interface]
PrivateKey =
ListenPort = 51820
Address = 10.5.4.1/32

[Peer]
PublicKey =
AllowedIPs = 10.5.4.25/32

[Peer]
PublicKey =
AllowedIPs = 10.5.4.20/32
To add another user just add another [Peer] section.
Then install your client App.
My client conf:
[Interface]
Address = 10.5.4.25
PrivateKey =
#DNS = 10.5.5.1 #Server caching dnsmasq that forwards to azure
#DNS = 168.63.129.16 #Azure
DNS = 1.1.1.1 #Cloudflare

[Peer]
PublicKey =
Endpoint = <serverip>:51820
#Endpoint = 127.0.0.1:59401
#AllowedIPs = 0.0.0.0/0
AllowedIPs = 10.5.4.1/32

# This is for if you're behind a NAT and
# want the connection to be kept alive.
PersistentKeepalive = 25
To generate a keypair for your client I use:
wg genkey | tee privatekey | wg pubkey > publickeyTo turn your conf file into a qr code use:
qrencode -t ansiutf8 < wg0.confPoint your remote desktop software to 10.5.4.1 instead of the server’s public IP.
Don’t forget to close the RDP port if it’s still open to the internet.
]]>- Change BIOS to boot when power comes back up.
- Install Ubuntu Desktop
https://ltsp.github.io/docs/installation/ - Install LTSP
https://ltsp.github.io/docs/installation/ - Create interface bridge:
https://netplan.io/examples#configuring-network-bridges
Example bridge config.
sudo nano -w /etc/netplan/01-netcfg.yaml# This file describes the network interfaces available on your system
# For more information, see netplan(5).
network:
version: 2
renderer: networkd
ethernets:
eno1:
dhcp4: no
bridges:
br0:
addresses:
- 10.0.16.25/24
gateway4: 10.0.16.1
nameservers:
search: [mydomain, otherdomain]
addresses: [10.0.16.1, 1.1.1.1]
interfaces:
- eno1- Install KVM
sudo apt install virt-manager Install Windows VM
- Download Windows
- Create QEMU/KVM Virtual Machine.
- Be sure to Disk bus under Disk hard drive type to VirtIO.
- Be sure to change NIC device model to “virtio”
- Be sure to select the bridge you set up.
- Confirm There is a “Display Spice” and “Video QXL”
- Attach both Windows 2016 ISO and the VIRTIO driver ISO downloaded from here:
https://fedorapeople.org
Install FreeRDP nightly
https://ci.freerdp.com/job/freerdp-nightly-binaries/
- /groups/virt/virtio-win/direct-downloads/stable-virtio/virtio-win.iso
- Install Windows server, and choose custom to choose the Win2k16 version. Select the CD-rom drive the was attached and navigate to the prospective folders.
- Balloon
- NetKVM
- vioserial
- Viostor
- Install networking driver from iso. Install virtio serial, and virtio balloon driver. If not done in the above step by simple going to device manager, and right clicking to choose update driver. Choose browse my computer and point it to the iso. be sure to click include sub directories.
- Install Display driver QXL by going to Device mananger Display update driver
- Install QEMU “guest-agent” from iso
- Install spice-guest-tools from:
https://www.spice-space.org/download/windows/spice-guest-tools/spice-guest-tools-latest.exe
Configure VM for remote desktop
- Change serial, and activate Windows 2016
- Enable Windows Audio service and set to automatic.
- Rename Computer.
- Set static IP.
- Allow remote desktop through firewall.
- Connect to existing Domain for User Authentication, or set up a new one:
https://social.technet.microsoft.com/wiki/contents/articles/22622.building-your-first-domain-controller-on-2012-r2.aspx - Install Remote Desktop Services
https://community.spiceworks.com/how_to/122824-install-terminal-services-on-windows-server-2012-r2 - Install Remote Desktop Licenses
https://social.technet.microsoft.com/wiki/contents/articles/37408.setup-rd-licensing-role-on-windows-server-2012-r2.aspx - Add Users.
Configure thin client
- Setup the RDP client
https://github.com/ltsp/community/wiki/xfreerdp
All you have to do is:
- Install steam
- sudo apt install steam
- Got to settings, and “Enable Steam Play for all titles”
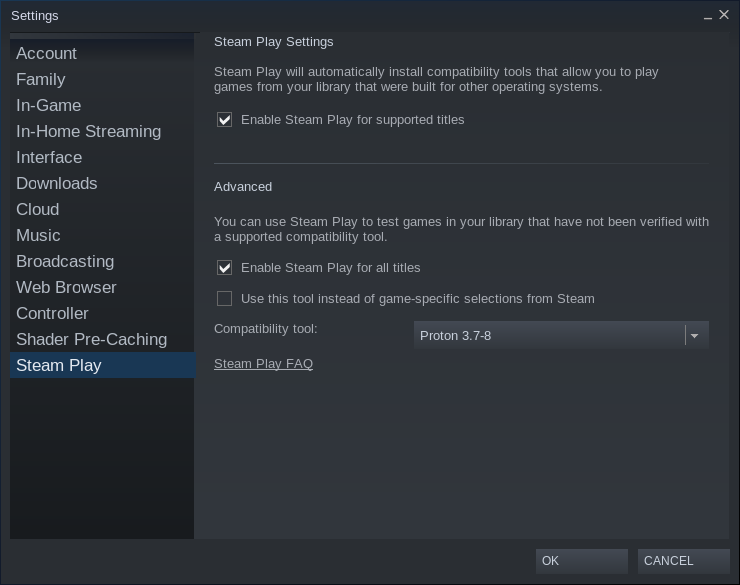
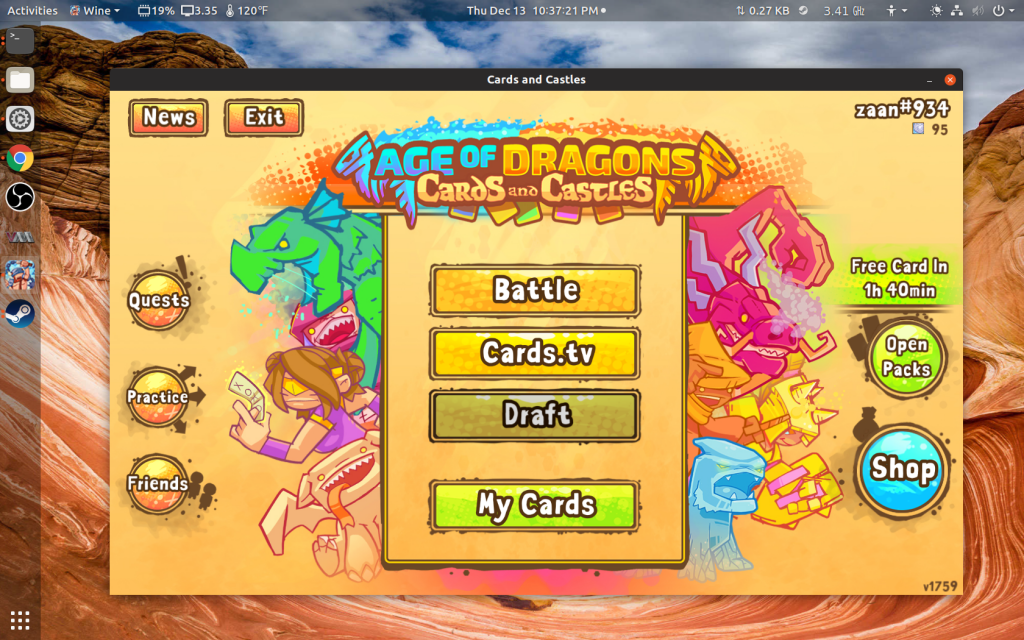
To install, simply run the below commands in a terminal:
sudo apt-add-repository -y ppa:teejee2008/ppa
sudo apt-get install ukuu
Then in dash call “ukuu”
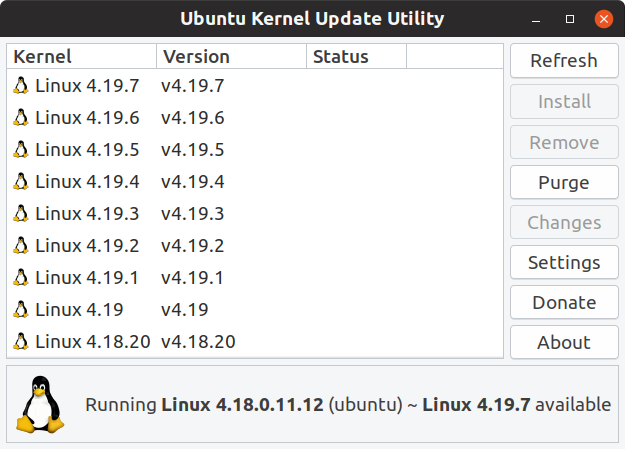
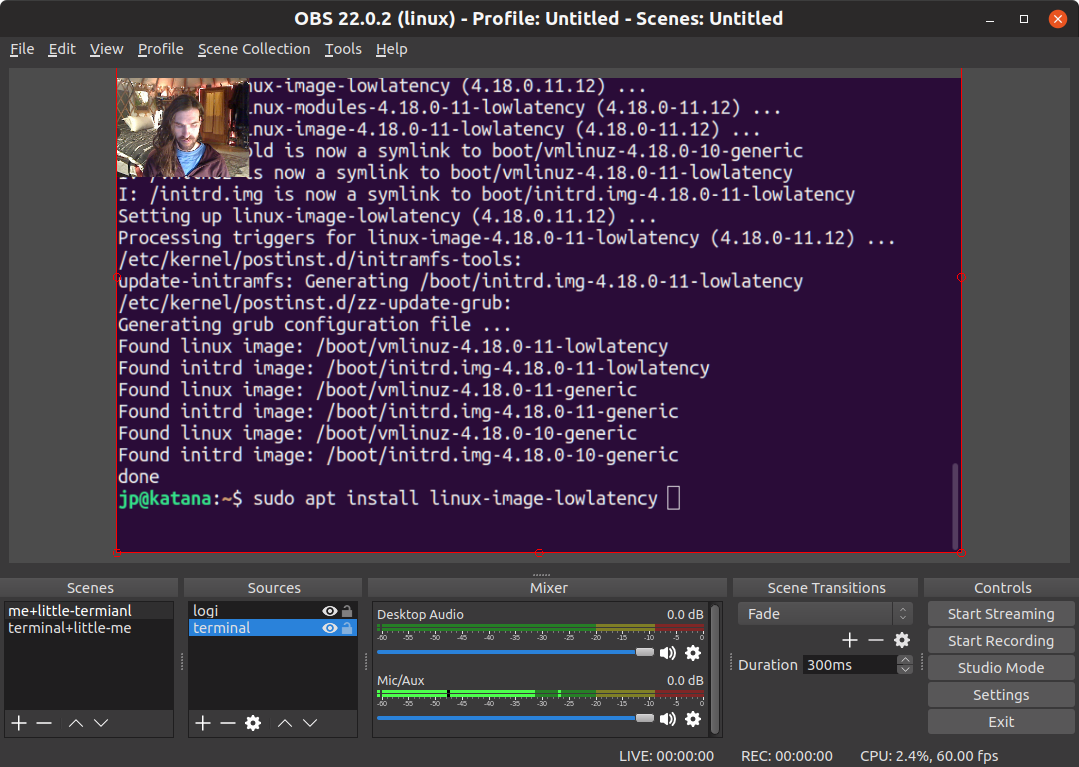
This evening I will be showing you how to install Open Broadcaster Software, aka OBS on Ubuntu 18.10 Cosmic Cuttlefish.
This is useful for recording or streaming how to’s such as these, or any other content.
When recording audio in Ubuntu, you can install the low latency kernel image for lower [wiki]latency[/wiki]/delay. It is an example of a soft real-time computing kernel. It is my understanding that this kernel sacrifices stability for low latency. https://en.wikipedia.org/wiki/Real-time_computing#Criteria_for_real-time_computing
Run the below commands in a terminal.
1. Install the low latency kernel
sudo apt --yes install linux-image-lowlatency
2. Install the OBS ppa
sudo apt-add-repository --yes ppa:obsproject/obs-studio

sudo apt --yes install ffmpeg obs-studio
3. Reboot the computer to start using the new low latency kernel.
After reboot confirm you’re using the low latency kernel:
uname -r
4.18.0-11-lowlatency
4. Run OBS from dash:
However if you are interested in the PXE boot menu, and netbooting into a Ubuntu install here is some great info:
Alternatively,
<pre>#Add to MAC of second server your existing dhcp conf to tell it to run the installer by default when it PXE boots
[<mac address>]
filename /ubuntu-installer/amd64/pxelinux.0
#Log in remotely into second server, after install
ssh ubuntu@<ip from dhcp syslog> -p ubuntu
</pre>
General Info
* Create PXE menu installer for both client and server.
* Client –> LTSP menu (default)
* Install boxen baby (wifi or vpn remote) client — ubuntu bionic desktop minimal install with xfreerdo-ngihtly
* Install boxen brain server — preseeded ubuntu with boxen install script
* Boot first HD
* netboot.xyz https://netboot.xyz/booting/tftp/
https://wiki.ubuntu.com/UEFI/PXE-netboot-install
https://help.ubuntu.com/community/UbuntuLTSP/LTSPMultiboot
* Create Preseed file for PXE installers.
https://diegolemos.net/2017/08/06/pxe-booting/
https://help.ubuntu.com/lts/installation-guide/example-preseed.txt
https://gist.github.com/skx/ecc3a429eb11a3c7f022
https://help.ubuntu.com/lts/installation-guide/armhf/apbs02.html
https://www.syslinux.org/wiki/index.php?title=PXELINUX
#ltsp: This is the place for support of LTSP. Ask your question and hang around for an answer. Check IRC logs at http://irclogs.ltsp.org
[19:56] == jphein [b8178628@gateway/web/freenode/ip.184.23.134.40] has joined #ltsp
[19:56] -ChanServ- [#ltsp] Welcome to the Linux Terminal Server Project's irc channel
[19:58]  Hello to everyone. =] I have a nice LTSP install in KVM. It's using Ubuntu 18.04.1, with the chrootless dnsmasq proxy method
[19:59]  However, when I run ltsp-update-kernels my pxe config doesn't pick up the changes I make in /etc/ltsp/udpate-kernels.conf
[20:00]  my /var/lib/tftpboot/amd64pxelinux.cfg/ directory remains unchanged
[20:01]  When I make the changes directly in the files it works well
[20:09]  Am I missing something?
[21:56]  jphein: yes, /usr/share/ltsp/update-kernels
[21:56]  This transfers /etc/ltsp/update-kernels.conf to /boot/pxelinux.cfg/default
[21:56]  Then ltsp-update-image puts it in /opt/ltsp/images/amd64.img
[21:57]  And finally ltsp-update-kernels gets it from amd64.img and puts it to tftp
[21:57]  Thank you! I'll try it out. =]
[21:57]  It's so complicated that I wanted to get rid of it and just use a static file :D
[21:59]  hahaha
[22:08]  So it never goes to /var/lib/tftpboot/ltsp/amd64/pxelinux.cfg/ ?
[22:17]  I'd like to install Ubuntu as a pxe option before my ltsp menu
[22:32]  jphein: sure, it goes to pxelinux.cfg after the 4 steps I mentioned above
[22:38]  lol!
and
#ltsp: This is the place for support of LTSP. Ask your question and hang around for an answer. Check IRC logs at http://irclogs.ltsp.org
[21:36] == jphein [b8178628@gateway/web/freenode/ip.184.23.134.40] has joined #ltsp
[21:36] -ChanServ- [#ltsp] Welcome to the Linux Terminal Server Project's irc channel
[21:37]  Hello! =] Does anyone know where I would put my install-ubuntu kernels so that update-kernels picks them up and presents them on the PXE menu?
[21:39]  Or, do I have to edit the pxelinux.cfg/default symlink manually?
[21:39] == vagrantc [~vagrant@unaffiliated/vagrantc] has joined #ltsp
[21:41]  This is my https://github.com/jphein/boxen/blob/master/etc/ltsp/update-kernels.conf
[21:44]  I suppose I can edit my dnsmasq.d/ to add the mac address of the client I'd want to install. With the ubuntu-install pxe boot config.
[21:48]  I'm also having issues with the chrootless method in the Azure cloud. Seems the Azure kernel may not have all the right input drivers for KVM?
[22:25]  jphein: I'm not sure what you're asking; why do you need more than one kernel?
[22:25]  If you only keep one kernel, then ltsp will pick them up
[22:26]  Now if you want multiple kernels, ltsp will pick up the latest
[22:26]  Sorry, let me rephrase that. Do you know of a simple way to present the PXE client user with a menu to install Ubuntu?
[22:26]  So if e.g. azure has 4.1, and you manually install 4.15, then the server will have 4.1 and the clients 4.15, without involving any configs
[22:26]  cool
[22:26]  jphein: ah sure, you just expose the .iso etc
[22:27]  But the "ltsp way to install a client" is to netboot it and cp -a /run/initramfs/rofs /target
[22:27]  I.e. to clone the ltsp image...
[22:27]  that's exactly what i want
[22:28]  You can also easily netboot it, and run: kvm -cdrom /path/to/windows -hda /dev/sda, so that you can even install windows while booted as an ltsp client
[22:28]  All those don't involve pxelinux at all
[22:28]  You do those via epoptes after the client boots normally via ltsp
[22:28]  oh yes kvm
[22:28]  (or locally)
[22:29]  with epoptes
[22:29]  nice
[22:29]  I usually don't want to leave my chair, so I do all clients via epoptes
[22:29]  haha =]
[22:29]  So I can be installed 3 different OSes on 3 clients without me going there
[22:30]  *I can install, meh
[22:30]  I can be installing. OK, got it :P
[22:30]  thank you , again!
[22:30]  np
[22:30]  I like that solution a lot.
[22:31]  Do you know the simplest way to preseed an Ubuntu installation with a few changes?
[22:32]  wcp -a /run/initramfs/rofs /target
[22:32]  Do I make a screen script?
[22:33]  jphein: let's clear something up
[22:34]  cp is for cloning the ltsp image
[22:34]  kvm is for installing ubuntu from an .iso
[22:34]  preseeding only applies to the iso
[22:34]  So which one are you asking about?
[22:35]  hahaha, I'm just very curious
[22:35]  =]
[22:35]  i like all of them
[22:35]  but I want to know more about the cp -a
[22:35]  it's a simple as that?
[22:36]  cloning
[22:36]  I don't make screen scripts for such simple things; I do make scripts that I run either from epoptes or directly from the client
[22:36]  cp, add user, install grub
[22:36]  You can also have a vm on the server, and use dd, to avoid all that
[22:36]  oh i see
[22:37]  using qcow?
[22:37]  or raw img
[22:37]  E.g. I have bionic-mate in vbox, then i expose it via nbd, and I dd if=/dev/nbd2 of=/dev/sda on the clients, and it's ready
[22:37]  Both can be done, qemu-nbd supports qcow and vdi and vmdk and raw
[22:38]  so many ways
[22:38]  that is the one i'll use since I already have the vm
[22:38]  You can even login normally as a user on the client, so that your image is accessible by sshfs in /home/username
[22:38]  So then you do dd if=/home/username/vms/myvm of=/dev/sda, done
[22:38]  No scripts, no screen scripts, nothing
[22:39]  You may only need to resize2fs /dev/sda1 afterwards, so that it extends to all the disk size
[22:39]  right
[22:41]  and you're doing this in a user with sudo privledges or something?
[22:41]  yes
[22:41]  Yup, with LDM_HASH_PASSWORD=True; or via epoptes :)
[23:34]  Which commands do you run after a cp -a /run/initramfs/rofs /target ? Install grub?
[00:16]  jphein: mount /dev/sda1 /mnt; cd /mnt; for d in proc sys dev dev/pts; do mount --bind /$d $d; done; chroot . dpkg-reconfigure grub-pc; umount dev/pts dev sys proc
]]>
Manual: NXW116QC264-User-Manual
Requirements:
- You will need an Ubuntu computer to perform these steps
- An USB flash drive >= 4GB capacity
- OTB USB micro adapter
- Download Ubuntu the desktop iso here: https://www.ubuntu.com/download/desktop
Commmands:
wget https://github.com/kenorb-contrib/isorespin/raw/master/isorespin.sh

chmod u+x isorespin.sh

./isorespin.sh -i ubuntu-18.10-desktop-amd64.iso --atom
Steps:
- Insert a USB and make a note of which device it is (use
df,blkidorlsblkto confirm). - Unmount any files systems auto mounted from the USB:
sudo umount /dev/sdx* - Write the respun ISO to USB:
sudo dd if=ubuntu-18.10-desktop-amd64.iso of=/dev/sdx bs=4M - Plug flash drive into Flexx with OTB USB Micro adapter.
- Reboot into Boot Manager. I used the cmd terminal method from windows 8.1:
shutdown.exe /r /o
Resources:
https://github.com/kenorb-contrib/isorespin
http://linuxiumcomau.blogspot.com/2017/06/customizing-ubuntu-isos-documentation.html
]]>As you can see from the matrix below there are MANY ways of providing desktops to your users.
However, I think this way has many advantages for a Nonprofit. I would recommend it generally, although of course other topographies are more useful in specific situations.
Benefits for a Nonprofit
- Green computing – Thin clients use less power than traditional workstations.
- Reduced maintenance costs – Thin client deployment means you’re only maintaining a couple servers, instead of multiple traditional workstations. Using Azure cloud means you don’t have to maintain server hardware.
- 100% free horizontal software – Completely free Open Source horizontal market software.
- Discounted vertical market software – Purchase heavily discounted MS remote desktop licenses at Techsoup. Along with anything else you might need. e.g. Quickbooks, MS Office, and any other vertical market software. https://www.techsoup.org/
- $3500 Azure Credit, Free Office 360 – Free cloud servers, Office.
Apply for Microsoft Nonprofit here: https://nonprofit.microsoft.com/register - Free Voice,Gsuite,etc.. – Free cloud Telephony, calendaring, file management, and email with custom domain.
Apply for Google Nonprofit here: https://www.google.com/nonprofits/ - Free hardware; Nevada County among others will donate their old computers, and peripherals to any eligible local nonprofit. Perfect for blazingly fast thin clients. Bring your tax exempt paperwork to the warehouse on the last Friday of the month. Or, try Purchasing hardware from your local government entity here: https://www.publicsurplus.com/sms/nevadacounty,ca/list/current?orgid=315996 After that try eBay: https://rover.ebay.com/rover/1/711-53200-19255-0/1?mpre=https%3A%2F%2Fwww.ebay.com%2Fb%2FPC-Desktops-All-In-One-Computers%2F179%2Fbn_661752&campid=5337848787&toolid=20008
- No taxes – If you use Comcast as your internet provider, make sure to file tax exemption paperwork with them to waive the applicable taxes. Email tax exempt certificate to: [email protected] . Include service address & account #.
- 50% off internet – If you are school, or other eligible nonprofit in California sign up here for 50% off your internet bill. https://jphein.com/discounted-phone-and-internet-for-nonprofits-in-california/
Terms
- [wiki]Vertical market software[/wiki] – https://en.wikipedia.org/wiki/Vertical_market_software
- [wiki]Thin client[/wiki] – https://en.wikipedia.org/wiki/Thin_client
- [wiki]Linux Terminal Server Project[/wiki] (LTSP) – https://en.wikipedia.org/wiki/Linux_Terminal_Server_Project
- [wiki]Ubuntu[/wiki] – https://en.wikipedia.org/wiki/Ubuntu
- [wiki]Remote Desktop[/wiki]
Guide
Follow along. At the end of this guide you should be able to plug in any number of old computers without hard drives into your local network. Then have them boot blazingly fast Windows based modern software. Wireless, and remote VPN clients are also supported.
In this setup all thin clients will be sharing a single Windows 2016 Datacenter instance. However, you can provide any number of environments using this method, including huge VDI deployments. My favorite is using LTSP Ubuntu fat client desktops with RemoteApps for seamless cloud integration of necessary windows based proprietary software.
I am using Ubuntu 18.04 Bionic Beaver for the LTSP server, because LTSP does not currently work with Ubuntu 18.10 Cosmic Cuttlefish.* In my case the entire setup was virtualized in the Azure cloud using KVM Virtual Machine Manager for virtual thin clients.
It might look like this:
[Azure Standard D4s v3[[PXE thin client – KVM guest] –> [Ubuntu 18.04] LTSP Server]] –>[Azure Standard NV6 [Windows 2016]]
In real life the more likely scenario would be to install Ubuntu on a bare metal server onsite. Then, install Ubuntu 18.04 inside a KVM vm. Plug a thin client into your network, and configure it for PXE boot in BIOS. It would look a little like this:
[PXE thin client] –> [[Ubuntu 18.10] [Ubuntu 18.04 KVM guest LTSP server]] –> [Firewall] –> [Internet] –> [Azure Standard NV6 [Windows 2016]]
In this guide I will be first showing you how to set up the virtualized system, and then go into some changes you’ll need to make in the field.
Requirements
- An internet connection. 3MB/s or more recommended.
- A computer with keyboard and display capable of running at least SSH. To issue the commands from.
- A computer capable of running Ubuntu with at least one network card. Or a virtual machine capable of nested virtualization like the Azure Standard D4s v3. For the LTSP server.
- A virtual or real windows machine locally or in the cloud. You’ll need Remote desktop licenses if you want to use microphone forwarding. If using Azure, not every region has the NVIDIA Tesla servers (NV6) for hardware graphics rendering. USA South Central is what I used. This is used for the desktop environment.
IPs
- 10.0.0.1 – Gateway.
- 10.0.0.5 – eth0 – Local interface on Ubuntu server – Connected to the Internet.
- 192.168.122.1 – virbr0 – Virtual bridge on Ubuntu server for testing virtual thin clients.
- 10.0.0.4 – Windows 2016 datacenter RDP server with NV6 Nvidia Tesla hardware.
Create your Azure Virtual Machines
After signing up and being accepted to Microsoft Nonprofit, verify your $3500 credit here: https://www.microsoftazuresponsorships.com/Balance
Create your virtual machines here: https://portal.azure.com
Note: DO NO USE accelerated networking on the Ubuntu Server.
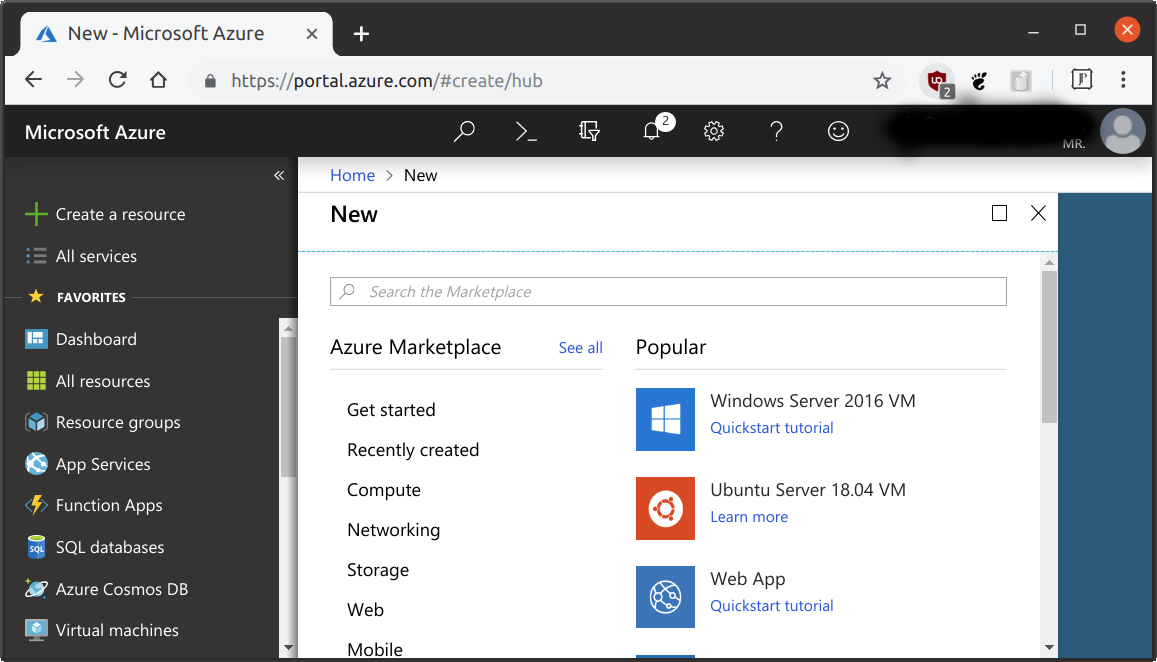
LTSP Server
- Image type: Ubuntu 18.04
- Size: Azure Standard D4s v3
Desktop Server
- Image type: Windows 2016 Datacenter
- Size: Azure Standard NV6
[jbox]Azure comes with a premade Ubuntu 18.04 image, but if you are doing this in the field you would need to install Ubuntu on your server:
Install Ubuntu 18.04.1 Desktop (Minimal)
- Ubuntu 18.04.1 Desktop.
- Download ISO here: https://www.ubuntu.com/download/desktop
- Install the desktop version, minimal install.
- Instructions here: https://jphein.com/how-to-install-ubuntu-18-04-18-10-to-an-usb-3-1-m-2-16gb-drive-using-kvm/
If you decide to have a local Windows server instead or in addition to the Azure vm, you’ll need to install Windows locally.
Install Windows 2016 Datacenter
- Download ISO from Microsoft Volume Licensing Center
- Install
[/jbox]
Configure Windows 2016 Datacenter
Configure remote desktop for microphone redirection:
- Install Remote Desktop Session Host
- You’re either still inside the grace period OR have the Remote Desktop Licensing role installed and a valid CAL
- Make sure the remote desktop group policy allows audio recording
Configure graphics acceleration: https://lg.io/2016/10/12/cloudy-gamer-playing-overwatch-on-azures-new-monster-gpu-instances.html
Configure the Ubuntu and install LTSP Server
[jbox]You can find a bash script automating all the below commands here: https://raw.githubusercontent.com/jphein/boxen/master/boxenbrain [/jbox]
To manually install BoXenLinux we will be configuring LTPS using the Chrootless Proxy mode for in the field. It is the easiest of the 4 ways to install LTSP. However, for the Azure cloud we’ll need to install using a chroot.
[jbox color=green]Set a static IP for your wired network interface in the field
Microsoft azure VM comes with the static IP set on your default interface. However, in the field you’ll need to set a static IP address.
https://www.itzgeek.com/how-tos/linux/ubuntu-how-tos/netplan-how-to-configure-static-ip-address-in-ubuntu-18-04-using-netplan.html
https://netplan.io/examples
[/jbox]
Optional: Install OpenSSH server
If using the Azure install as the LTSP server, you’ll want to overwrite the existing sshd_config so that you can using password login if you used a key when creating the VM.
sudo apt install ssh
Install LTSP and epoptes (epoptes lets you remote desktop in and help anyone using a thin client), Instructions from http://wiki.ltsp.org/wiki/Installation/Ubuntu:
sudo add-apt-repository --yes ppa:ts.sch.gr #The Greek Schools repository
sudo apt install --yes --install-recommends ltsp-server-standalone ltsp-client epoptes
Configure dnsmasq
Note: You may want to edit the /etc/dnmasq.d/ ltsp-server-dnsmasq.conf and add “dhcp-option=3,192.168.122.1” to set a different gateway, but probably not.
sudo ltsp-config dnsmasq --enable-dns
sudo service dnsmasq restart
Add yourself the epoptes group
sudo gpasswd -a ${SUDO_USER:-$USER} epoptes
Was told to remove these packages
sudo apt purge --yes --auto-remove mate-hud snapd
[jbox color=blue title=”Optional: Chroot Install”]
Build a chroot client for alternate arch, dekstop enviroment or package base
Grab freerdp’s key
cd /etc/ltsp
sudo wget http://pub.freerdp.com/repositories/ADD6BF6D97CE5D8D.asc
- Option 1 – with command
sudo ltsp-build-client --purge-chroot --mount-package-cache --mirror 'http://azure.archive.ubuntu.com/ubuntu/'
 --apt-keys '/etc/ltsp/ADD6BF6D97CE5D8D.asc, /etc/apt/trusted.gpg.d/ts_sch_gr_ubuntu_ppa.gpg'
 --extra-mirror 'http://ppa.launchpad.net/ts.sch.gr/ppa/ubuntu bionic main, http://pub.freerdp.com/repositories/deb/bionic/ freerdp-nightly main'
 --late-packages epoptes-client freerdp-nightly --prompt-rootpass --fatclient
- OR, Option 2 – using my ltsp-build-client.conf
sudo wget https://github.com/jphein/boxen/raw/master/etc/ltsp/ltsp-build-client.conf
sudo ltsp-build-client --config ltsp-build-client.conf
You may want to install a new kernel like this one if the azure kernel doesn’t work with all of KVM’s input drivers:
sudo apt-get install linux-image-lowlatency
Then you have to edit the update-kernels.conf file, so that LTSP chooses that one to boot the client.
Create some symlinks so freerdp-nightly is more easy t my lazy scripting
sudo ltsp-chroot
ln -s /opt/freerdp-nightly/bin/xfreerdp /usr/bin/xfreerdp-nightly
ln -s /usr/share/ltsp/screen.d/xfreerdp /usr/share/ltsp/screen.d/xfreerdp-nightly
exit
Create GUI login screen for xfreerdp-nightly (Not updated!)
cd /opt/ltsp/amd64/usr/share/ltsp/screen.d/

sudo wget https://raw.githubusercontent.com/jphein/boxen/master/rdpgui

sudo wget https://raw.githubusercontent.com/jphein/boxen/master/xfreerdp-prompt

sudo chmod +x rdpgui xfreerdp-prompt
sudo ltsp-update-image
Note: You may get this error on Microsoft Azure VM! https://bugs.launchpad.net/ubuntu/+source/ltsp/+bug/1802707 hmmmm…. This script seems to fix it:
#!/bin/bash
# tadaen sylvermane | jason gibson
# configure locales for ubuntu bionic ltsp chroot creation


for var in LC_ALL= LANG= ; do
        export "$var"en_US.UTF-8
done
ltsp-build-client --chroot "$1"
[/jbox]
[jbox color=green title=”Local Chrootless Install”]
This is the recommended, and simplest install
Install FreeRDP-nightly and client zenity GUI
sudo sh -c 'echo "deb http://pub.freerdp.com/repositories/deb/$(lsb_release -cs)/ freerdp-nightly main" >> /etc/apt/sources.list.d/freerdp-nightly.list'
wget -O - http://pub.freerdp.com/repositories/ADD6BF6D97CE5D8D.asc | sudo apt-key add -
sudo apt update
sudo apt install --yes freerdp-nightly
sudo ln -s /opt/freerdp-nightly/bin/xfreerdp /usr/bin/xfreerdp-nightly
cd /usr/share/ltsp/screen.d/
sudo ln -s xfreerdp xfreerdp-nightly
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/usr/share/ltsp/screen.d/rdpgui
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/usr/share/ltsp/screen.d/xfreerdp-prompt
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/usr/share/ltsp/screen.d/launch
sudo mkdir boxen
cd boxen
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/usr/share/ltsp/screen.d/boxen/welcome
cd ..
sudo ln -s launch welcome
sudo ln -s /sbin/shutdown shutdown
sudo chmod +x rdpgui xfreerdp-prompt launch boxen/welcome
Create LTSP client NBD image using the chrootless method of the servers root /
You need to run this any time you make changes to your filesystem you want to be updated in your LTSP client.
sudo ltsp-update-image --cleanup /
[/jbox]
Grab the lts.conf for our thin clients
cd /var/lib/tftpboot/ltsp/amd64/
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/var/lib/tftpboot/amd64/lts.conf
Edit lts.conf to suit your needs
nano -w lts.conf
Test with KVM virtual pxe thin client
If you are already using KVM to install Ubuntu in a VM then you don’t need to install it again. However, if you are using a real bare metal server then you’ll need to run the install command.
sudo apt install virt-manager
[jbox]Libvirtd will run dnsmasq on virbr0 by default. We need to kill that instance and restart the global dnsmasq with our LTSP configs. You will need to killall and restart dnsmasq every time you reboot.
###dnsmasq hack for testing
sudo mv /etc/dnsmasq.d/libvirt-daemon /root/
sudo sh -c 'echo "dhcp-range=192.168.122.20,192.168.122.250,8h" >> /etc/dnsmasq.d/ltsp-server-dnsmasq.conf
#These steps will need to performed again if you reboot
sudo killall dnsmasq
sudo service dnsmasq restart
[/jbox]
#Create the PXE test KVM client
sudo virt-install
  --name pxe
  --memory 4096
  --vcpus 2
  --disk none
  --pxe
  --os-variant ubuntu17.10
  --wait 0
Connect locally using very nice spice
virt-viewer --connect qemu:///system pxe
Connect remotely using spice
virt-viewer --connect qemu+ssh://[email protected]/system pxe


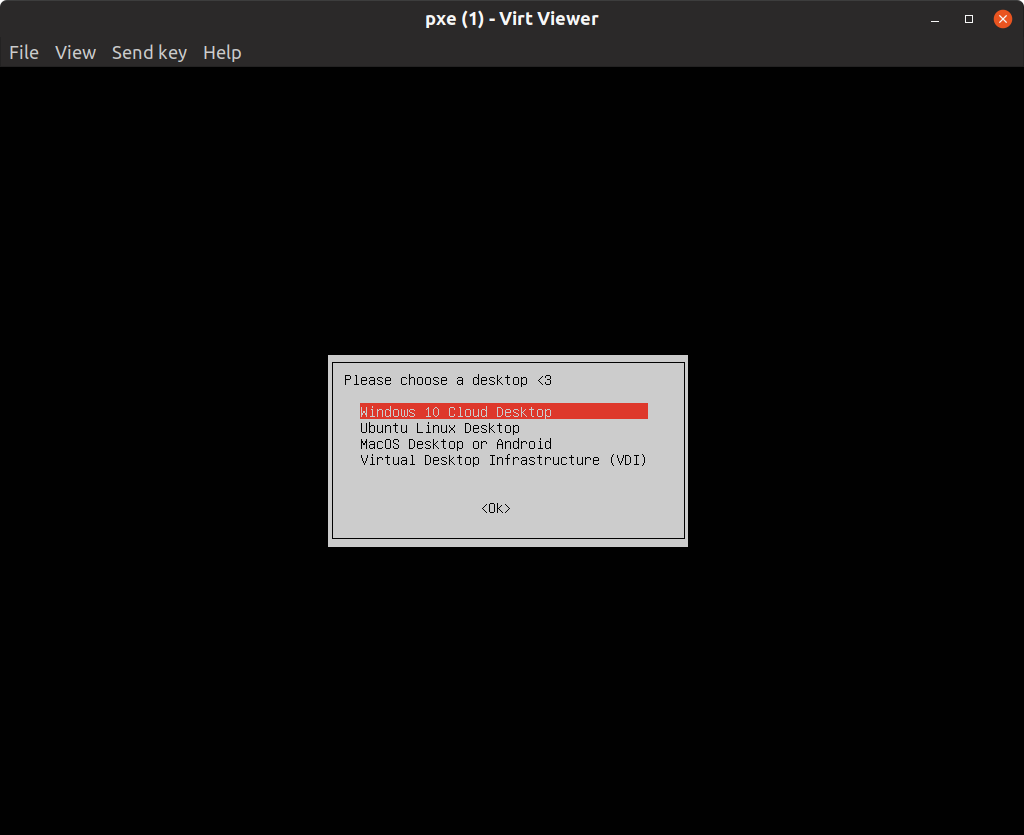
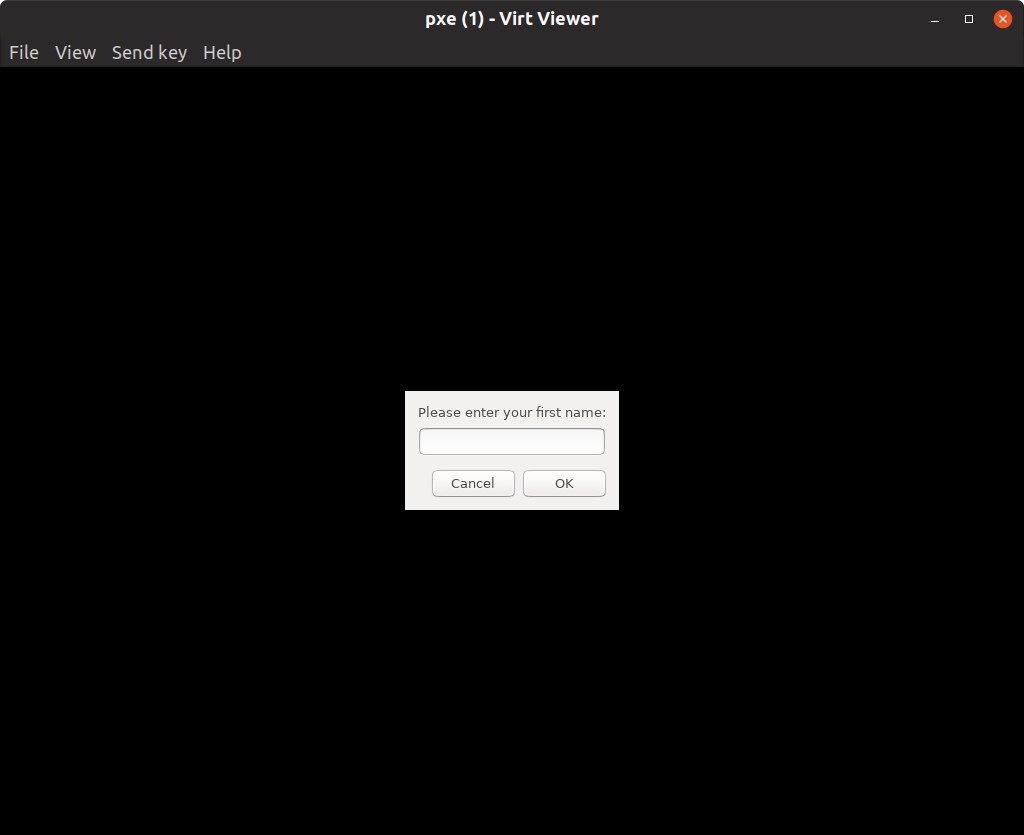
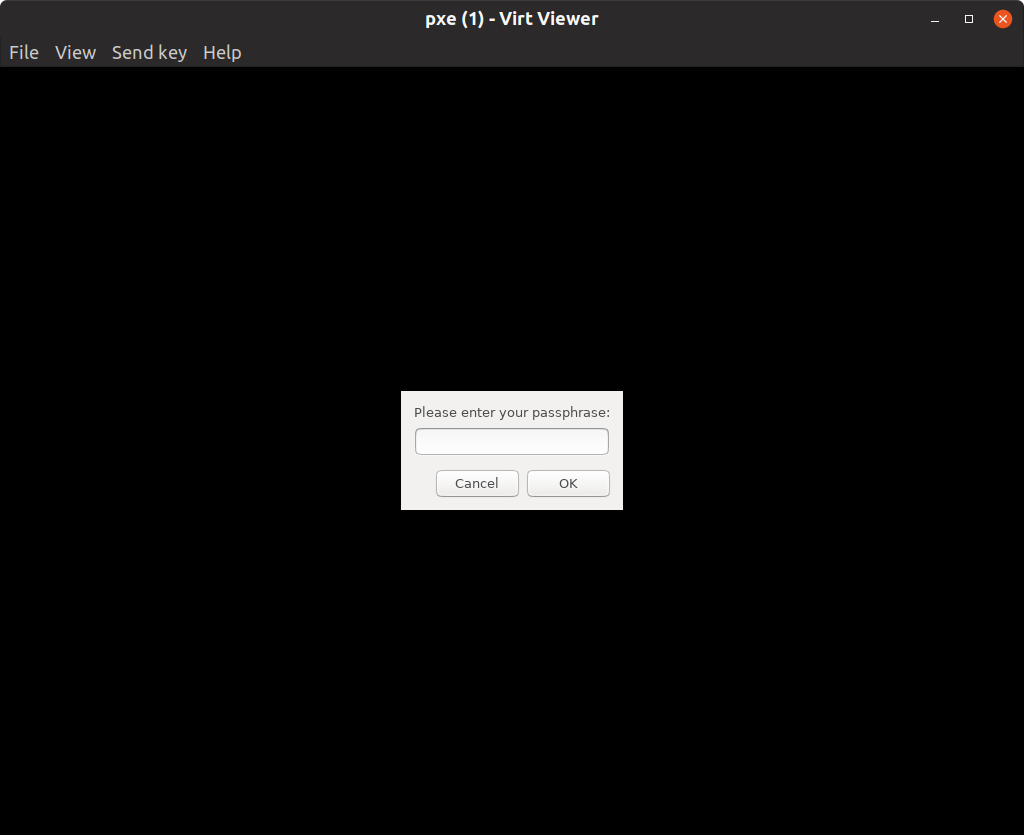
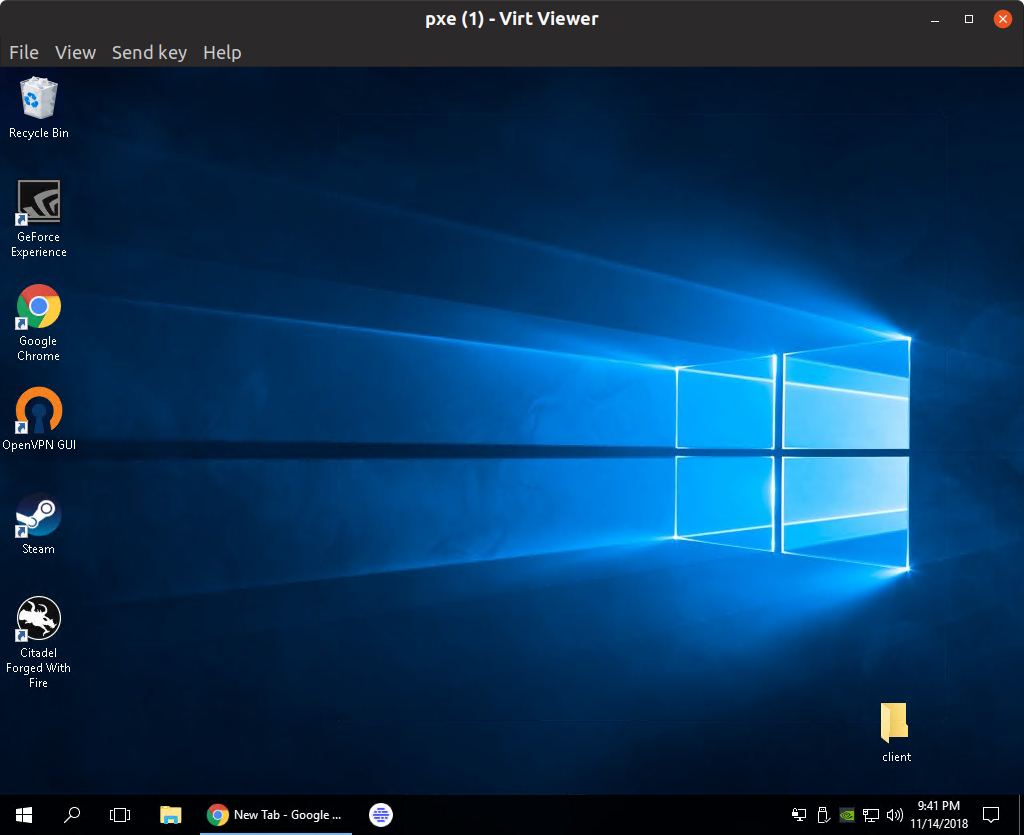 Tada!!!
See also
lts.conf manpage ltsp-build-client manpage ltsp-update-image manpage ltsp-config manpage ltsp-chroot manpage http://wiki.ltsp.org/wiki/Installation/Ubuntu https://help.ubuntu.com/community/HowToSetupLTSPDevelEnvironment https://github.com/wyllianbs/xfreerdp-gui https://unix.stackexchange.com/questions/119880/make-freerdp-prompt-user-for-username-and-password/187370 http://www.saminiir.com/debugging-pxe-boot/
* Ubuntu 18.10 I previously tried this with Ubuntu 18.10 Cosmic Cuttlefish, and ran into some issues. Mainly the maintainer of LTSP for Ubuntu does not fix anything that is not a LTS release.
Optional Install ltsp-manager
sudo add-apt-repository --yes ppa:franz-die/ltsp-manager; apt update

sudo apt install ltsp-manager
Optional: Install X2Go remote desktop software
sudo add-apt-repository ppa:x2go/stable
sudo apt-get update
sudo apt-get install x2goserver x2goserver-xsessions x2gomatebindings
Optional: Install Ubiquity to install Ubuntu on PXE booted clients or servers
sudo apt-get install ubiquity ubiquity-frontend-gtk
Running it is a manner of running from the client
ubiquity gtk_ui
Optional: Add iPXE to grub menu
apt install grub-ipxe
[jbox]Optional: Set up Firewall with IP Masquerading
Probably won’t need to do this.
First, packet forwarding needs to be enabled in ufw. Two configuration files will need to be adjusted, in /etc/default/ufw change the DEFAULT_FORWARD_POLICY to “ACCEPT”:
sudo nano -w /etc/default/ufw #change DEFAULT_FORWARD_POLICY="ACCEPT"
Then edit /etc/ufw/sysctl.conf,
sudo nano -w /etc/ufw/sysctl.conf
and uncomment:
net/ipv4/ip_forward=1
net/ipv6/conf/default/forwarding=1
Now add rules to the /etc/ufw/before.rules file. The default rules only configure the filter table, and to enable masquerading the nat table will need to be configured. Add the following to the top of the file just after the header comments:
sudo nano /etc/ufw/before.rules
# nat Table rules
*nat
:POSTROUTING ACCEPT [0:0]
# Forward traffic from eth1 through eth0.
-A POSTROUTING -s 192.168.122.0/24 -o eth0 -j MASQUERADE
# don’t delete the ‘COMMIT’ line or these nat table rules won’t be processed
COMMIT
Allow SSH
sudo ufw allow 22
sudo ufw allow from 192.168.122.0/24
sudo ufw enable
[jbox]
Optional: Install apt-cacher
apt-cacher will cache packages so you don’t waste your time downloading them again again.
sudo apt install apt-cacher
sudo nano /etc/apt-cacher/apt-cacher.conf #Uncomment allowed_hosts= *
sudo ufw allow 3142/tcp
sudo sh -c 'echo "Acquire::http::Proxy "http://10.0.0.5:3142"";' > /etc/apt/apt.conf.d/01proxy
sudo /usr/share/apt-cacher/apt-cacher-import.pl -l /var/cache/apt/archives
sudo service apt-cacher restart
Optional: Test with QEMU
Set up virtual bridge for client networking
On the azure VM I was able to use the default virtual bridge virbr0. Just commented out the dnsmasq.d/ file libvirt that prevented dnsmasq from serving IPs on that network. However, testing on a real server I needed to make my own bridge. These commands should not be issued if working on your server remotely. Only a local bare metal install should issue these commands.
sudo ip tuntap add dev virttap mode tap user $USER
sudo brctl addbr virtbr
sudo brctl addif virtbr eth0 # your LAN interface
sudo brctl addif virtbr virttap
sudo ip link set virtbr up
sudo ip link set eth0 up
sudo ip link set virttap up
dhclient virtbr
You may need to restart dnsmasq again
sudo service dnsmasq restart
Run QEMU to test your LTSP setup
cd
qemu-img create -f vmdk testpxe.vmdk 10
/usr/bin/qemu-system-x86_64 -m 1024 -hda testpxe.vmdk
                              -boot n
                              -option-rom /usr/share/qemu/pxe-rtl8139.rom
                              -net nic
                              -net tap,ifname=virttap,script=no,downscript=no
]]>