Preparation:
- Sign up for a free Gmail.com account
- Sign up for Cloudflare.com
Steps:
- Register your domain with Cloudflare
- Add your website to Cloudflare
- Configure DNSEC, SPF, DKIM, and DMARC with Cloudflare
- DNSEC is easy if your domain is registered with Cloudflare
- Configure SPF to include Google (support.google.com/googleapps), and your own website IP address.
- Set up DKIM
- Set up DMARC
- Set up email forwarding in Cloudflare to your Gmail account
- Set up “send as” address in Gmail
- Test sending and receiving email with your custom domain through your Gmail account
- Check your email deliverability score at mail-tester.com
More Reading:
- help.17hats.com/en/articles/2933143-how-to-set-up-email-forwarding-with-cloudflare
- dmarcly.com/blog/how-to-use-dmarc-to-protect-your-domain
Note: This guide assumes that you have already signed up for a Gmail account and Cloudflare account.
Email security is important to protect your organization from phishing attacks and email fraud. There are several email security features that you can enable for your custom domain, including DNSSEC, SPF, DKIM, and DMARC. DNSSEC is a security protocol that authenticates DNS data and can help prevent DNS spoofing attacks. SPF is a security protocol that helps to prevent email spoofing by verifying that email messages come from authorized senders. DKIM is a security protocol that uses digital signatures to verify the authenticity of email messages. DMARC is a security protocol that helps to prevent email spoofing by verifying the alignment of SPF and DKIM policies. Enabling these email security features for your custom domain can help to protect you from email fraud and phishing attacks. As well as make sure that your legitimate email is not marked as spam.

Preparation
Sign up for a free gmail.com account. Google has the best deliverability, and spam filters in my experience. I’d recommend signing up for cloudflare.com as well. They have the lowest cost domain registration as well. $8/year. They have a really good free account for everything else. They can help you set up the below domain, and email settings:
- DNSSEC
- SPF
- DKIM
- DMARC
- Email forwarding to your gmail account.
Steps
- Sign up for gmail.com, protonmail.com, or your own mail server.
- Sign up for cloudlfare.com
- Register your domain with cloudflare
- Add your website to cloudflare
- Configure DNSEC, DKIM, SPF, and DMARC with cloudflare.
- DNSEC is easy if domain is registered with cloudflare.
- DKIM
- SPF (make sure to include google in your SPF) https://support.google.com/googlecloud/answer/10756302
- DMARC
- Set up email forwarding in cloudflare to your gmail account
- Set up “send as” address in Gmail
- Test
- Test sending and receiving email with your custom domain through your gmail account.
- Test email deliverability score at https://www.mail-tester.com/
More reading
https://help.17hats.com/en/articles/865530-how-to-ensure-emails-do-not-end-up-in-spam
]]>Federal Level:
- Supplemental Nutrition Assistance Program (SNAP) (previously known as Food Stamps)
- Temporary Assistance for Needy Families (TANF)
- Medicaid
- Housing Choice Voucher Program (Section 8)
- Low-Income Home Energy Assistance Program (LIHEAP)
- Supplemental Security Income (SSI)
- Child Care and Development Fund (CCDF)
- National School Lunch Program (NSLP)
- Women, Infants, and Children (WIC) Program
- Earned Income Tax Credit (EITC)
- Community Services Block Grant (CSBG)
- Head Start
- Older Americans Act (OAA) Programs
- Supplemental Nutrition Program for Women, Infants, and Children (WIC)
- Children’s Health Insurance Program (CHIP)
- Social Services Block Grant (SSBG)
State of California:
- CalWORKs (California Work Opportunity and Responsibility to Kids)
- California Food Assistance Program (CFAP)
- CalFresh (California’s Supplemental Nutrition Assistance Program)
- In-Home Supportive Services (IHSS)
- California Emergency Assistance and Rapid Transition to Housing (CEART)
- Energy Assistance Fund (EAF)
- Low-Income Home Energy Assistance Program (LIHEAP)
- Women, Infants, and Children (WIC) Program
- School Breakfast and Lunch Programs
- Medicaid (Medi-Cal)
- Health Care for Kids and Families (HCKF)
- Child Care Assistance
- Earned Income Tax Credit (EITC)
- Section 8 Housing Choice Voucher Program
- Community Services Block Grant (CSBG)
- Social Services Block Grant (SSBG)
- Head Start
- Older Americans Act (OAA) Programs
Nevada County, California:
- Nevada County Food Bank
- Interfaith Food Bank
- Nevada County Health and Human Services Agency
- Western Sierra Medical Clinic
- Chapa De Clinic
- Hospitality House
- The Salvation Army of Nevada County
Nonprofit services in Nevada County, California
- Hospitality House
- The Salvation Army of Nevada County
- Community Legal Services of Empowerment
- Interfaith Food Ministry
- Nevada County Free Clinic
- The Resource Connection
- Hospice of the Foothills
- Sierraservice Corps
- Western Sierra Medical Clinic
- Women’s Health Specialists
- Nevada County Nurtured Heart Approach
- Sierra Senior Services
- Boys and Girls Club of Western Nevada County
- Grass Valley Food Co-op
- Nevada County Volunteer Center
- Friends of Nevada County Libraries
- Sierra Nevada Memorial Hospital Foundation
Note: This is not an exhaustive list, and program names, eligibility criteria, and benefits may vary by state.
My experience
I’m consistently amazed at the level of assistant you can get from government, and non-profit organizations if you make less than 21K-40K a year. Here are programs I’ve had personal experience with. Also, some extra money saving tips.
For a comprehensive list of services (Dial 211 or visit www.dial211.com) I feel like their website is very hard to navigate. If it was better than there would be no need for this blog post.
Bottom Line: Minimize buying, but when you do, buy used and buy locally. For instance: Gold Country Craigslist, Nevada County Swap Shop Facebook group, thrift stores, yard sales, and sort by distance on eBay.
Cash Aid
- Calworks
- Unemployment
- Disability or Paid family leave
- Business grants
- Supportive Services
Food
We are incredibly lucky. We have an immense good food network. I only eat organic, non-GMO, no sugar and local meat.
- Food banks (Staples, as well as organic, local produce)
- Interfaith Food Ministry – open every Mon, Wed, and Fri. You can go every two weeks. Bring your social security card your first visit. Be sure to return any food you do not want before you leave. http://www.interfaithfoodministry.org/
- NC food bank – Open once a month, view calendar here: Calendar
- Food stamps (EBT or Calfresh) Sign up online – 1-877-847-3663. I get around $200/month.
- TIP: If you’re in a hurry, at Natural Selections you can buy locally premade Way Yum sushi, Theresita’s Haute Tamales, or Warehouse deli sandwiches with your EBT card!
- TIP: You can use EBT at the Nevada City Farmers Market
- TIP: You can use EBT to mail order food from Amazon or Walmart.
- Markets: Nevada City farmers Market, EBT, and $25 free voucher.
- Stores: Grocery outlet (Pick out the organic food), Natural Selections (Clearance shelves)
- Free School Lunch Program
- WIC if you are pregnant or have a child you can get food and a free breast pump. They also provide tokens for the Nevada City farmers’ market.
TIP: Save your vegetable scraps and meet scraps in the freezer to make vegetable and bone sock respectively.
TIP: Eat your food in the order that it will perish. Regularly eat all the food in your fridge.
TIP: Save your bacon grease. Cook with it, or make soap.
TIP: Nut/seed/grain milk is super easy to make. Kefir/Yogurt. Kombucha/jun. SaurKraut/Kimchi, Sprouts.
More info here: http://211nevadacounty.org/resources/food/
Housing
Federal Subsidized housing
Grass Valley First Time Home Buyer Program
Nevada County Habitat For Humanity Homeownership Program
Nevada County weatherization program Project Go call 1-800-655-7705
PGE Weatherization program
Habit for humanity REstore
Regional Housing Authority of Sutter and Nevada County
Utilities
PG&E Care program – Gives a discount on Electricity and Natural Gas
Project Go For Energy Assistance, please call 1-888-524-5705 – Will pay your PG&E for a year, and/or will provide vouchers for wood, or propane.
Ferrelgas w/ neighborhood association or refurbished tank.
TIP: Composting toilet
TIP: Dryer lint and tp rolls for firestarters
TIP: Dry your clothes on a line!
TIP: Use cold water to wash your clothes.
TIP: If you use the dryer, add a dry towel with your wet clothes to speed up drying, or use wool dryer balls.
Phone and cellphone
California and Federal Lifeline programs – A free cellphone and service, or a discount on your landline. For more info check out my article here: The Cell Phone Guru blog post
(Sprint) Freedompop – 200 Voice Minutes 500 Text Messages 500MB 3G/4G Data with $99 phone +$10 s/, OR activate your own Sprint phone for $20. Not limited to low income users.
Google Voice with Hangouts and dailer- free wifi calling for your smart phones or computers. Not limited to low income users.
MVNO’s: Republic Wireless (Sprint, Verizon, Wifi), Pageplus (Verizon), Airvoice (ATT) Not limited to low income users.
Internet
More info here: http://www.cheapinternet.com/low-income-internet
(Sprint) Freedompop – 500MB/month 4G connection free with $30 + $10 s/h hotspot purchase. Not limited to low income users.
(Sprint) Netzero – 200MB/month for a year.$76.90 for device and s/h. Not limited to low income users.
(T-mobile) http://basic-internet.com/everyoneoncampaign/ – $10/month hotspot for $62.51 1.2GB at 4G speed, then unlimited at 3G for month.
(Comcast) http://www.internetessentials.com/ – Most have a child that qualifies for some school lunch program. Actually you have tons of options if you qualify for school lunch programs.
(Sprint) https://yourkarma.com/
(ATT) Sonic – semi-local DSL company
Gas
TIP: Gasbuddy
scooter
electric bicycle
bicycle
Medical
Medi-cal @ Western Sierra Medical Center General and dentist, vision dr. moon, equine therapy
Women’s health specialist w/ qwest and fee waiver
Vehicle Insurance
Minimum insurance or
Pay as you go: Metromile
Banking
FirstUS Credit Union – Free checking and savings
River Valley Community Bank – Free checking and savings
School
Sierra College: FAFSA, Governor Fee Waiver
Business
Nevada City Small Business Loans and Grant
David Nelson – Nevada City CDBG Program Manager
http://nevadacityca.gov/sites/all/modules/tinytinymce/tinymce/jscripts/tiny_mce/plugins/filemanager/files/admin/EconomicDevel.pdf
Sierra commons
Kickstarter Indiegogo, etc…
Website hosting
HangLeft Hosting
Software:
Ubuntu
Open source software
Sundries
Use white vinegar to clean everything
Make your toothpaste
Use soap nuts for soap or make it
Use apple cider vinegar and baking soda to wash hair, coconut oil to condition
coconut oil for all lotion, moistorizer, sunblock
Use reusable toilet rags instead of toilet paper
Petfood: Animalsave program or make your own.
Make cloth bags for bulk items and produce
Store vegetables in cloth bags or dish towels
More resources
These are the programs that I personally use. A resourced, single, white male living in Western Nevada County. If you are a person without reliable transportation, a person without a permanent home, a person with two X chromosomes, a person with children, a person with a disability, a person suffering from chronic illness, a person who has suffered violence, a person suffering from addiction, a person that has served in the military, a person with more than 65 years under your belt, of you live in Eastern Nevada County, check out the site below where you will find even more services.
Nevada County Community Resource Directory (available 24 hours a day)
Emergency Assistance Coalition (EAC)
877-847-0499 (Dial 211 / www.dial211.com)
You can view Nevada County’s 2014-2015 Cummunity Action Plan (CAP) that was created so that we could receive the $1.6M Federal CSBG* grant that helps fund these services here: CAP. Note: Each non-profit that applied and was approved got $60K/year for 2 years.
*The Community Services Block Grant (CSBG), administered by the states, provides core funding to local agencies to reduce poverty, revitalize low-income communities and to empower low-income families to become self-sufficient.
]]>A domain name can contain all 26 letters, 10 numbers, and a hyphen (-). You cannot start or end a domain name with a hyphen. Domain names are not case sensitive, so you can use upper and lower case letters interchangeably. A domain name can be up to 67 characters long — including the 4 characters used to identify the Top Level Domain (.net, .com or .org).
A little known fact is that you CAN have multiple dashes right next to each other. (e.g. domain--names.com) Opened up a few more possibilities? There is one restriction: Double Hyphens in the third and fourth position are not allowed. e.g. XX--XXXXXXXX.com. This allows for IDNs and other encodings.Results
All three letter .com domains are taken. However, there are still 3 character .net and .org domain names.
.com – All three character .com names are registered.
.net – All three letter, or all 3 number names are taken. All LLN (Letter Letter Number) or anything with a hyphen is taken.
.org – All three letter, or all three 3 number names are taken NNN.org, and LLL.org. All L-L.org domains are taken. Checked the N-L.org, L-N.org, and N-N.org. Looks like there are a number of hyphenated 3 charactor .org domains left, but they all contain numbers.
I just wrote and ran a bash scripts to check all three character .org domains.
#!/bin/bash
#All three character .org domains with a hyphen in the middle
for x in {0..9} {a..z}; do
	for y in "-"; do
		for z in {0..9} {a..z}; do
			domnf=""
			domnf=$(whois $x$y$z.org|grep "Domain not found.")
			if [ "$domnf" == "Domain not found." ]; then
				echo $x$y$z.org
			fi
			domnf=""
			sleep 1
		done
	done
done
Complete list of available hyphenated three character .org (N/L-N/L.org) domain names:
0-5.org
0-8.org
0-c.org
0-e.org
0-h.org
0-i.org
0-j.org
0-l.org
0-m.org
0-q.org
0-s.org
0-t.org
0-u.org
0-v.org
0-w.org
0-y.org
0-z.org
1-d.org
1-e.org
1-f.org
1-l.org
1-n.org
1-p.org
1-r.org
1-s.org
1-u.org
1-y.org
2-8.org
2-9.org
2-e.org
2-f.org
2-i.org
2-j.org
2-l.org
2-m.org
2-n.org
2-p.org
2-w.org
2-x.org
2-z.org
3-1.org
3-j.org
3-n.org
3-o.org
3-t.org
3-u.org
3-z.org
4-1.org
4-b.org
4-f.org
4-g.org
4-n.org
4-o.org
4-v.org
4-x.org
4-z.org
5-0.org
5-8.org
5-9.org
5-c.org
5-e.org
5-f.org
5-j.org
5-l.org
5-n.org
5-o.org
5-q.org
5-s.org
5-t.org
5-u.org
5-w.org
5-x.org
5-y.org
5-z.org
6-2.org
6-8.org
6-a.org
6-b.org
6-c.org
6-d.org
6-f.org
6-g.org
6-h.org
6-i.org
6-j.org
6-k.org
6-l.org
6-m.org
6-n.org
6-o.org
6-p.org
6-q.org
6-r.org
6-s.org
6-u.org
6-w.org
6-x.org
6-y.org
6-z.org
7-2.org
7-b.org
7-e.org
7-h.org
7-j.org
7-l.org
7-n.org
7-o.org
7-p.org
7-s.org
7-u.org
7-v.org
7-w.org
7-y.org
8-1.org
8-4.org
8-7.org
8-a.org
8-c.org
8-e.org
8-f.org
8-g.org
8-j.org
8-l.org
8-m.org
8-n.org
8-r.org
8-t.org
8-u.org
8-v.org
8-w.org
8-x.org
8-y.org
8-z.org
9-1.org
9-8.org
9-c.org
9-e.org
9-f.org
9-g.org
9-i.org
9-j.org
9-k.org
9-l.org
9-m.org
9-n.org
9-o.org
9-p.org
9-q.org
9-r.org
9-s.org
9-t.org
9-u.org
9-v.org
9-y.org
9-z.org
a-6.org
b-5.org
b-6.org
b-8.org
c-2.org
c-7.org
c-9.org
d-0.org
d-4.org
d-5.org
e-0.org
e-6.org
f-0.org
f-6.org
f-7.org
f-8.org
f-9.org
g-6.org
g-7.org
g-9.org
h-0.org
i-6.org
j-0.org
j-7.org
j-9.org
k-0.org
l-4.org
l-5.org
l-9.org
m-0.org
n-0.org
n-4.org
o-3.org
o-5.org
o-9.org
p-0.org
p-2.org
p-4.org
p-6.org
p-7.org
q-0.org
q-2.org
q-3.org
q-6.org
r-0.org
r-7.org
r-8.org
r-9.org
s-6.org
s-8.org
t-5.org
t-8.org
t-9.org
u-0.org
u-3.org
u-5.org
v-0.org
v-1.org
v-3.org
v-7.org
w-1.org
w-4.org
w-7.org
x-6.org
x-8.org
y-0.org
y-1.org
y-8.org
y-9.org
z-0.org
z-3.org
z-4.org
z-5.org
Looks like there are still LNL LLN and NLL .org domains left as well.
#!/bin/bash
#All three character .org domain names with numbers and letters.
for x in {0..9} {a..z}; do
	for y in {0..9} {a..z}; do
		for z in {0..9} {a..z}; do
			dom=""
			dom=$(whois $x$y$z.org|grep "Domain not found.")
			if [ "$dom" == "Domain not found." ]; then
				echo $x$y$z.org >> domainlist.txt
			fi
			dom=""
			sleep 1
		done
	done
done
inComplete list of available non-hyphenated three character .org domain names: closed my laptop after the letter n.
Resources
Here is a report of cost of 3 character domain names for .com .net .org, etc.. http://www.3character.com/price-guide.html
Here is an OK search tool: http://www.namestall.com/3-4-letter-domains
]]>Some advantages of hosting your own custom WordPress website with Docker include: – You have full control over your website and can customize it however you want. – Docker makes it easy to set up and maintain your website. – You can run your website on any platform that supports Docker. – Your website will be more scalable and reliable than if it were hosted on a traditional web server.
Set up cloudflare
Create account, and add domains.
Set up google free tier instance:
From: https://cloud.google.com/free/docs/free-cloud-features
Set up billing notifications if it goes over $0.03
Compute Engine free tier
1 non-preemptible e2-micro VM instance per month in one of the following US regions:
Oregon: us-west1
Iowa: us-central1
South Carolina: us-east1

30 GB-months standard persistent disk

5 GB-month snapshot storage in the following regions:
Oregon: us-west1
Iowa: us-central1
South Carolina: us-east1
Taiwan: asia-east1
Belgium: europe-west1

1 GB network egress from North America to all region destinations (excluding China and Australia) per month
Your Free Tier e2-micro instance limit is by time, not by instance. Each month, eligible use of all of your e2-micro instance is free until you have used a number of hours equal to the total hours in the current month. Usage calculations are combined across the supported regions.

Compute Engine free tier does not charge for an external IP address.

GPUs and TPUs are not included in the Free Tier offer. You are always charged for GPUs and TPUs that you add to VM instances.

Learn more- Modify firewall
- remove rdp allow firewall rule
- modify ssh to only accept connections from cloudshell: 35.235.240.0/20
- allow from anywhere to ports 80,443
- (optional) allow port 51820 for wireguard
- Make swap file, and add to fstab: https://www.digitalocean.com/community/tutorials/how-to-add-swap-space-on-ubuntu-16-04
- (Optional) Install wireguard for VPN access: How to set up your own VPN using WireGuard on Ubuntu 21.10
Setup Dynamic DNS with Cloudflare
From: How to use Cloudflare for Dynamic DNS on Ubuntu 22.04
Install docker, and dependencies
From: https://docs.docker.com/engine/install/ubuntu/
##Set up the repository
#Update the apt package index and install packages to allow apt to use a repository over HTTPS:

sudo apt-get update

sudo apt-get install
    ca-certificates
    curl
    gnupg
    lsb-release

##Add Docker’s official GPG key:

sudo mkdir -p /etc/apt/keyrings
curl -fsSL https://download.docker.com/linux/ubuntu/gpg | sudo gpg --dearmor -o /etc/apt/keyrings/docker.gpg
#Use the following command to set up the repository:

echo
  "deb [arch=$(dpkg --print-architecture) signed-by=/etc/apt/keyrings/docker.gpg] https://download.docker.com/linux/ubuntu
  $(lsb_release -cs) stable" | sudo tee /etc/apt/sources.list.d/docker.list > /dev/null

#Install Docker Engine
#Update the apt package index, and install the latest version of Docker Engine, containerd, and Docker Compose, or go to the next step to install a specific version:

sudo apt-get update
sudo apt-get install docker-ce docker-ce-cli containerd.io docker-compose-plugin docker-compose
Install configurations
From: https://carlwillimott.medium.com/quickly-setup-wordpress-ssl-via-lets-encrypt-and-certbot-b29e8abf2072
git clone https://github.com/carlwillimott/docker-compose-wordpress-ssl.git
cd docker-compose-wordpress-ssl
nano -w docker-compose.yml
version: '3.3'

services:

  swag:
    image: linuxserver/swag
    container_name: swag
    restart: always
    depends_on:
      - wordpress
    volumes:
      - ./config:/config
      - ./default:/config/nginx/site-confs/default
    environment:
      - [email protected]
      - URL=blog.jphein.com
      - VALIDATION=http
      - TZ=America/Los_Angeles
      - PUID=1001
      - PGID=1002
    ports:
      - "443:443"
      - "80:80"

  wordpress:
    image: wordpress:latest
    container_name: wordpress
    hostname: wordpress
    depends_on:
      - db
    restart: always
    ports:
      - "8080:80"
    volumes:
      - ./www/:/var/www/html/
      - ./custom.ini:/usr/local/etc/php/conf.d/custom.ini
    environment:
      WORDPRESS_DB_HOST: db
      WORDPRESS_DB_USER: wp_db_user
      WORDPRESS_DB_PASSWORD: wp_db_pass
      WORDPRESS_DB_NAME: wp_db
      WORDPRESS_CONFIG_EXTRA: |
        define( 'WP_MEMORY_LIMIT', '96M' );

  db:
    image: mysql:5.7
    container_name: db
    volumes:
      - /var/lib/mysql:/var/lib/mysql
    restart: always
    ports:
      - "3306:3306"
    environment:
      MYSQL_ROOT_PASSWORD: mysql_root_pass
      MYSQL_DATABASE: wp_db
      MYSQL_USER: wp_db_user
      MYSQL_PASSWORD: wp_db_pass
Bring up the containers
docker-compose up -dMake the containers come up on boot
From: https://bootvar.com/systemd-service-for-docker-compose/
# Write systemd service in
nano -w /etc/systemd/system/mysite.service
[Unit]
Description=Service for mysite
Requires=docker.service
After=docker.service
[Service]
Type=oneshot
WorkingDirectory=/home/jp/jphein.com
Environment=COMPOSE_HTTP_TIMEOUT=600
ExecStart=/usr/bin/env /usr/bin/docker-compose -f /home/jp/jphein.com/docker-compose.yml up -d
ExecStop=/usr/bin/env /usr/bin/docker-compose -f /home/jp/jphein.com/docker-compose.yml stop
StandardOutput=syslog
RemainAfterExit=yes
[Install]
WantedBy=multi-user.targetNow you have created the systemd service, enable it and start the service. Enabling service will make sure to start this service at server startup.
# will enable service to start at server bootup
systemctl enable mysite

# start service ( Executes ExecStart command )
systemctl start mysite
Enable PageSpeed in WordPress docker
To be continued…
Configure WordPress
Go to yourdomain.com
Install WordPress Plugins
- Jetpack
- Jetpack boost
- Google Sitekit
- Cloudflare?
- Varnish? https://www.varnish-software.com/developers/tutorials/running-varnish-docker/
Test
Test SSL: www.ssllabs.com/ssltest/…
Test Pagespeed module: ismodpagespeedworking.co…
Test Varnish: https://isvarnishworking.uk/
Test your server response time: www.bytecheck.com
Should be 500ms or under. Ideally under 200ms.
Test email: https://www.mail-tester.com/
Forward your custom domain email to your gmail account
Cloudflare offers this service for free
Automated backups to Cloud storage bucket
Free tier
| Cloud Storage | 5 GB-months of regional storage (US regions only)5,000 Class A Operations per month50,000 Class B Operations per month1 GB network egress from North America to all region destinations (excluding China and Australia) per month |
|---|---|
Free Tier is only available in us-east1, us-west1, and us-central1 regions. Usage calculations are combined across those regions. |
Create a bucket in the google cloud console or terminal.
Install gcsfuse
Download .deb package frome: https://github.com/GoogleCloudPlatform/gcsfuse/releases
wget https://github.com/GoogleCloudPlatform/gcsfuse/releases/download/v0.41.6/gcsfuse_0.41.6_amd64.deb
sudo dpkg -i gcsfuse_0.41.6_amd64.deb
Permissions
You may need to run “gcloud init” if your permissions aren’t set up correctly. You may also need to edit your bucket permissions as well.
Mount bucket
From: https://github.com/GoogleCloudPlatform/gcsfuse/blob/master/docs/mounting.md
gcsfuse bucket_name mount_point
#unmount
fusermount -u /path/to/mount/point
Add to fstab to mount on boot
sudo echo "jphfree /home/jp/jphfree gcsfuse rw,_netdev,allow_other,uid=1001,gid=1002" >> /etc/fstab#Backup script
NOTE: If you want to use duplicity gs: urls then you should follow this guide: https://jphein.com/how-to-use-duplicity-to-backup-directly-to-a-google-cloud-storage-bucket-to-achieve-time-machine-like-incremental-backups-on-ubuntu-15-10-wily/
#Install mysqldump
sudo apt install mysql-client-core-8.0
#Install duplicity
sudo apt install duplicity
nano -w backup#!/bin/bash
#--A simple backup script
#----Change the variables below to reflect your information
echo "------------------------------------------------------------------"
echo " Website Backups"
echo "------------------------------------------------------------------"
echo "Creating variables..."
printf "$0 <-- Name and path of this script.n"
#Working directory
WD="/home/jp"
printf "$WD <-- Working Directory on local server.n"
echo "------------------------------------------------------------------"
#Google Cloud storage bucket"
printf "A Google Cloud storage bucket is used for longterm storage of incremental backups.n"
BUCKET="jphfree"
printf "$BUCKET <-- Google Cloud storage bucket namen"
echo "------------------------------------------------------------------"
#MySQL database
MYSQL_DB="wp_db"
MYSQL_USER="root"
MYSQL_PASS="db_root_pass"
printf "$MYSQL_DB <-- MySQL Database Namen"
printf "$MYSQL_USER <-- MySQL Database Usernamen"
echo "------------------------------------------------------------------"
#Google Cloud Storage Mount the storage bucket
printf "Mounting Google Cloud storage bucket...n"
gcsfuse $BUCKET $WD/$BUCKET
echo "------------------------------------------------------------------"
#MySQL dump
printf "Dumping MySQL database...n"
mysqldump --opt -h localhost --protocol=tcp --user=$MYSQL_USER --password=$MYSQL_PASS $MYSQL_DB > $WD/mysqldump/database.sql
echo "------------------------------------------------------------------"
#-------Duplicity Backup everything to the bucket
echo "------------------------------------------------------------------"
echo "Backing up data to a Google Gloud storage bucket using duplicity.."
echo "------------------------------------------------------------------"
echo "An incremental backup every day. A full backup every month."
echo "We keep 12 full backups and their corresponding incrementals."
echo "One year of daily back up data!"
echo "------------------------------------------------------------------"
#Clean up in case of aborted backups
duplicity cleanup --no-encryption file://$WD/$BUCKET/backups
#Backup data to bucket
duplicity --progress --no-encryption --exclude $WD/$BUCKET --full-if-older-than 1M $WD file://$WD/$BUCKET/backups
#Delete old backups
#duplicity remove-older-than 1Y --force $SYNC_DIR/$i gs://$BUCKET/$i
duplicity remove-all-but-n-full 12 file://$WD/$BUCKET/backups
#------------------------------------------------------------------------------chmod 700 backup#Add to crontab
crontab -e# Edit this file to introduce tasks to be run by cron.
#
# Each task to run has to be defined through a single line
# indicating with different fields when the task will be run
# and what command to run for the task
#
# To define the time you can provide concrete values for
# minute (m), hour (h), day of month (dom), month (mon),
# and day of week (dow) or use '*' in these fields (for 'any').
#
# Notice that tasks will be started based on the cron's system
# daemon's notion of time and timezones.
#
# Output of the crontab jobs (including errors) is sent through
# email to the user the crontab file belongs to (unless redirected).
#
# For example, you can run a backup of all your user accounts
# at 5 a.m every week with:
# 0 5 * * 1 tar -zcf /var/backups/home.tgz /home/
#
# For more information see the manual pages of crontab(5) and cron(8)
#
# m h dom mon dow command
0 0 * * * /home/jp/backup > /home/jp/backup.log 2>&1
Restore from Backups
duplicity restore file:///home/jp/jph-backups/backups /home/jp/restored/ --no-encryption
ATTENTION: I AM NO LONGER HELPING INDIVIDUALS SIGN UP FOR LIFELINE.
For questions call the Lifeline Administration here: https://www.cpuc.ca.gov/consumer-support/financial-assistance-savings-and-discounts/lifeline/california-lifeline-contacts
or, go to the lifeline website here: https://www.californialifeline.com/en
| Lifeline Provider | Cellular Network(s) | Website |
|---|---|---|
| Safelink Wireless | Verizon | https://www.safelinkwireless.com/ |
| StandUp Wireless | T-Mobile | https://www.standupwireless.com/ |
| TruConnect | T-Mobile | https://truconnect.com/ |
| Life Wireless | AT&T, T-Mobile | https://www.lifewireless.com/ |
| TAG Mobile | Verizon, T-Mobile | https://www.tagmobile.com/ |
| Access Wireless | T-Mobile | https://www.accesswireless.com/ |
| SafetyNet Wireless | T-Mobile | https://www.safetynetwireless.com/ |
| Feelsafe Wireless | AT&T | https://www.feelsafewireless.com/ |
| Assurance Wireless | T-Mobile | https://www.assurancewireless.com/ |
| American Assistance | ?Verizon, T-mobile? | https://americanassistance.com/ |
| Infiniti Mobile | ?AT&T,Verizon,T-mobile? | https://www.infinitimobile.com/ |
To create the above list, I cross referenced the California lifeline list here:
https://www.californialifeline.com/en/provider_search and here: https://cnm.universalservice.org/
with the Wikipedia article here:
https://en.wikipedia.org/wiki/List_of_United_States_mobile_virtual_network_operators
Safelink
NOTE: Since Verizon’s purchase of Movil the owner of Safelink, Net10, tracfone, pageplus. etc.. They only support the Verizon network.
I chose Safelink Wireless, because it is the only lifeline mobile virtual network operator who resells all 3 networks in California. You get unlimited talk, text, and data. As well as unlimited international calling to 69 countries. List of the 69 countries here: https://www.net10wireless.com/ilddestinations
Safelink also supports advanced features, such as: WiFi calling, WiFi texting (RCS), Hotspot, call forwarding, etc..
What you get!
The SIM card
You will get a T-mobile, Verizon, or AT&T SIM card depending on stock. You can tell by the first 5 numbers of the ICCD # on your phone box:
- 89148 Verizon
- 89012 TMobile
- 89014 ATT
The phone
NOTE: This information is outdated! You get a better phone now.
The free smartphone is the Alcatel TCL A2:
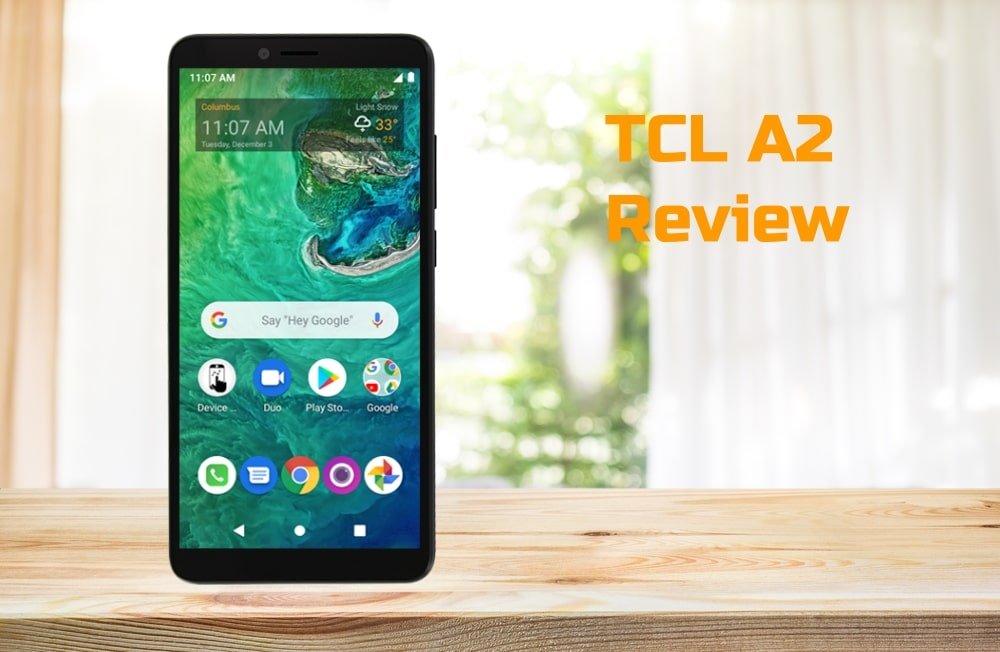
- OS: Android 10
- Screen size: 5.5-inch
- Resolution: 960 x 480
- CPU: 1.8GHz Quad-core processor
- RAM: 3GB
- Storage: 32GB
- Battery: 3000mAh, non-removable
- Rear camera: 8MP
- Front camera: 5MP
Full review here: https://tracfoneusermanual.net/tcl-a2-review/
Eligibility
You need proof of address, AND proof of eligibility. Here are some things you can use:
You need one of these :
- EBT card (Calfresh)
- Medi-cal card (The original one)
- TANF
- Calworks
- National school lunch program
- WIC
- Liheap
- SSI Awards letter
- Passport to Services ( A letter that the county can print out for you that states you’re receiving Medi-cal or Calfresh)
- Or, your 2020 tax return. Cannot be hand written. You must make less than 28,000 per year.
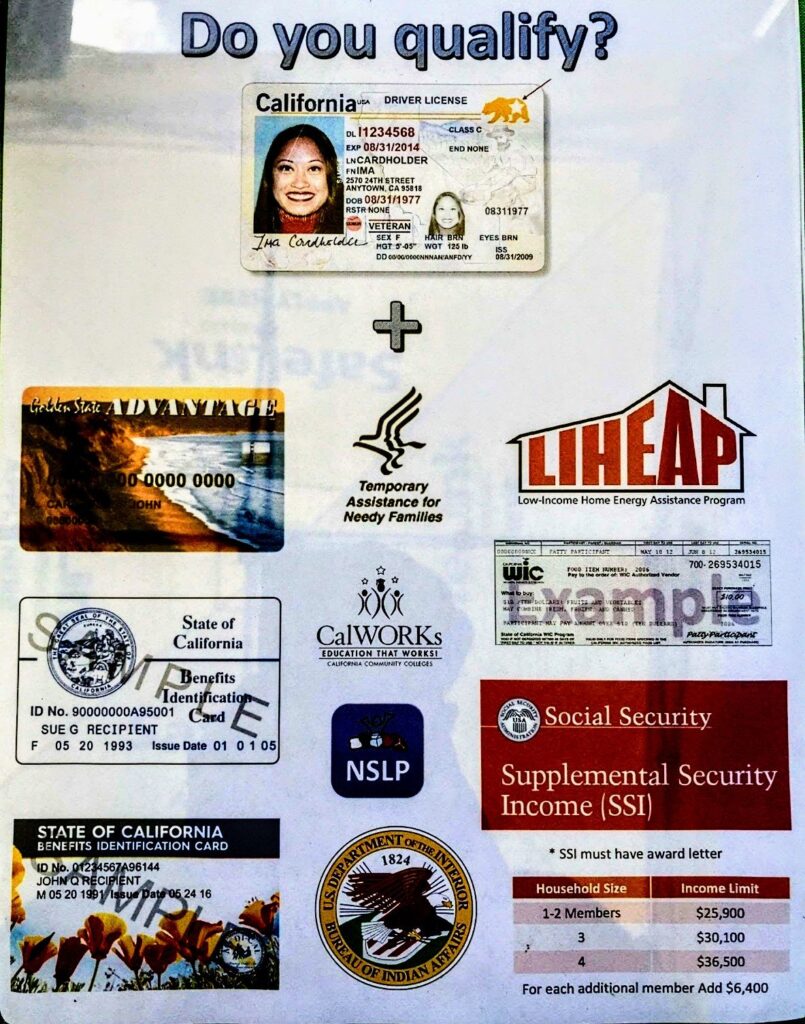
If your name, DOB, or social security number is not in their database then you’ll need a signed social security card, and a birth certificate, or ID.
Proof of Address
AND, you need one of these:
- Recent utility bill with name and address
- Current income statement from an employer,
- paycheck stub, or w-2 with name and address
- Prior year’s state, federal, or tribal tax return with name and address
- Current mortgage or lease agreement with name and address
- Unexpired California drivers licence
- Unexpired government, state, or tribal issued ID
- Government assistance program documents with name, address and effective dates
- Statement of benefits from a qualifying program with name, address and effective dates
- Retirement/pension statement of benefits with name and address
- Unemployment/workers’ compensation statement of benefits with name address and effective dates . Cal-Fresh and Medi-Cal verification of benefits form with name, address and effective dates
- Verification of receipt of Cal-fresh with name address, and date
- We can also use a “Verification of services letter” from a nonprofit. Make sure it has your name that matches your eligibility card. They will write in the letter that you are a client of theirs and receives assistance from their program. Make sure the name is printed, and the address is prominently displayed on organization letterhead.

If the address is not a valid residential address, you will need one of the below proofs:
- Recent Utility bill with the consumer’s name and address (not older than 90 days)
- Current income statement from an employer, paycheck stub, or W-2 with the consumer’s name and address
- Prior year’s state, federal, or Tribal tax return with the consumer’s name and address
- Current mortgage or lease statement with the consumer’s name and address
- Unexpired driver’s license
- Unexpired government, state, or Tribal issued ID
- Government assistance program documents with the consumer’s name, address, and effective date
- Statement of benefits from a qualifying program with the consumer’s name, address, and effective date
- Retirement/pension statement of benefits with the consumer’s name and address
- Unemployment/workers’ compensation statement of benefits with the consumer’s name, address, and effective date
Once you have your phone
Swipe right to access your home screen
Your new number will be in your text messages from 611611.
Make a call or text once a month to keep the service active.
Charge with included charger.
Look out for the pink letter welcoming your to the program.
Your recertification letter will come in 11.5 weeks.
It will take 5 days for ebb, your unlimited data and international calling to kick in.
Call 611 for customer service
Text ild to 611611 for the info. ItTo make International calls, dial 1-800-584-7652. or, You can download the International Dialer App here: iPhone: http://n10w.co/N9XmBm3 Android: http://n10w.co/NlVGgWq
Cancel it right away if you lose it. 1-800-safelin. Or call them to buy a new phone or sim card. I can give you a new phone 90 days after you cancel your service. Or, you can switch companies to get a new phone right away.
SafeLink uses NET10 sim cards. If you need a new one.
You can almost always port your old number in. It’s a federal law. More info here: https://www.fcc.gov/consumers/guides/porting-keeping-your-phone-number-when-you-change-providers Call 1800-safelin from a different phone.
Text 611611 one of the keywords found here: https://dsweb.safelink.com/611611/help/
SPEED To check if your data speed has been reduced, text the word SPEED to 611611
MINC To change your phone number, text the word MINC to 611611 or click here.
USAGE To see your current usage, text the word USAGE to 611611 or click here.
CHAT To get help through chat, text the word CHAT to 611611 or click here.
SUPPORT If you are experiencing issues with your service, text SUPPORT to 611611 or click here.
APP To download My SafeLink App, text the word APP to 611611 or Download your My Account app here: http://sflnk.co/L71Q4XZ
Free phones Nevada City, Grass Valley, Cedar Ridge, North San Juan, Penn Valley, Chicago Park, Camptonville, etc…
]]>Broadband: 25Mbps down, 3Mbps up, and less than 100ms latency.
Neither fiber nor cable is available where I live. All the fixed wireless providers in Nevada County don’t serve my property. AT&T will provide me a DSL line running at the insanely slow speed of 768kbps. That’s around 90 Kilobytes per second download, and don’t get me started on upload. Although, better than a 56K modem, it’s not fast enough for my needs. Geosynchronous satellite’s latency is too high for real time interaction. Low earth satellite is not available yet. AT&T is the only cellular provider with adequate coverage, however only on the new LTE band 14, all the other bands are spotty. FirstNet LTE Band 14 has been installed all over the Country by AT&T funded by a giant grant from the Federal government. My options are really quite limited. Luckily, I did eventually find something that works. Check out all the internet options in Nevada County here:
https://jphein.com/internet-options-in-nevada-county/
Here is a list of phones that have this LTE band 14:
https://www.firstnet.com/devices/phones.html
A complete list of devices is here:
https://www.firstnet.com/content/dam/firstnet/white-papers/firstnet-certified-devices.pdf
AT&T does not offer an inexpensive unlimited plan (<$100/month). Thus began my search for someone that did. I started out searching the Wiki article of all the MVNOs. (Mobile Virtual Network Operators) All the folks that resell time on the 4 major USA networks. I sorted it by the network column so I could filter all the AT&T MVNOs: https://en.wikipedia.org/wiki/List_of_United_States_mobile_virtual_network_operators
Then I found the article below,
https://www.rvmobileinternet.com/gear/att-unlimited-rental-plans/
which pointed me to:https://www.cgcellular.com/ Which provides unlimited data on AT&T for $60. Definitely the least expensive I’ve found. *No longer offering this. Instead check out how to get unlimted data for free here: jphein.com/lifeline
All AT&T Wireless unlimited plans supposedly deprioritize your data if your local cell tower is congested after 22GB. I don’t think it happens much in rural areas.
I purchase the Netgear Nighthawk M1 (MR1100) directly from my local AT&T store. Although, now you can buy one used on eBay.
Be sure to get the MR1100-2A1NAS model. The first consumer model does not support band 14. Read about it here: https://community.netgear.com/t5/Mobile-Routers-Hotspots-Modems/Pre-April-Nighthawk-and-band-14-and-46/m-p/1555303#M5746
It supports all LTE bands that AT&T uses. It was ~$270 with tax purchased outright. I put it on the $10/month for 100MB BYOD business plan. They waived any activation fee. I was able to unlock it after 60 days, and discontinued the original $10 plan.
https://www.att.com/deviceunlock/unlockstep1
Although, not necessary to unlock it for any AT&T reseller. I unlocked it in case in the future I need to use it with T-mobile, or Verizon.
Although currently locked to AT&T, I can use it with any AT&T MVNO by changing the APN setting from the web gui.
http://attwifimanager/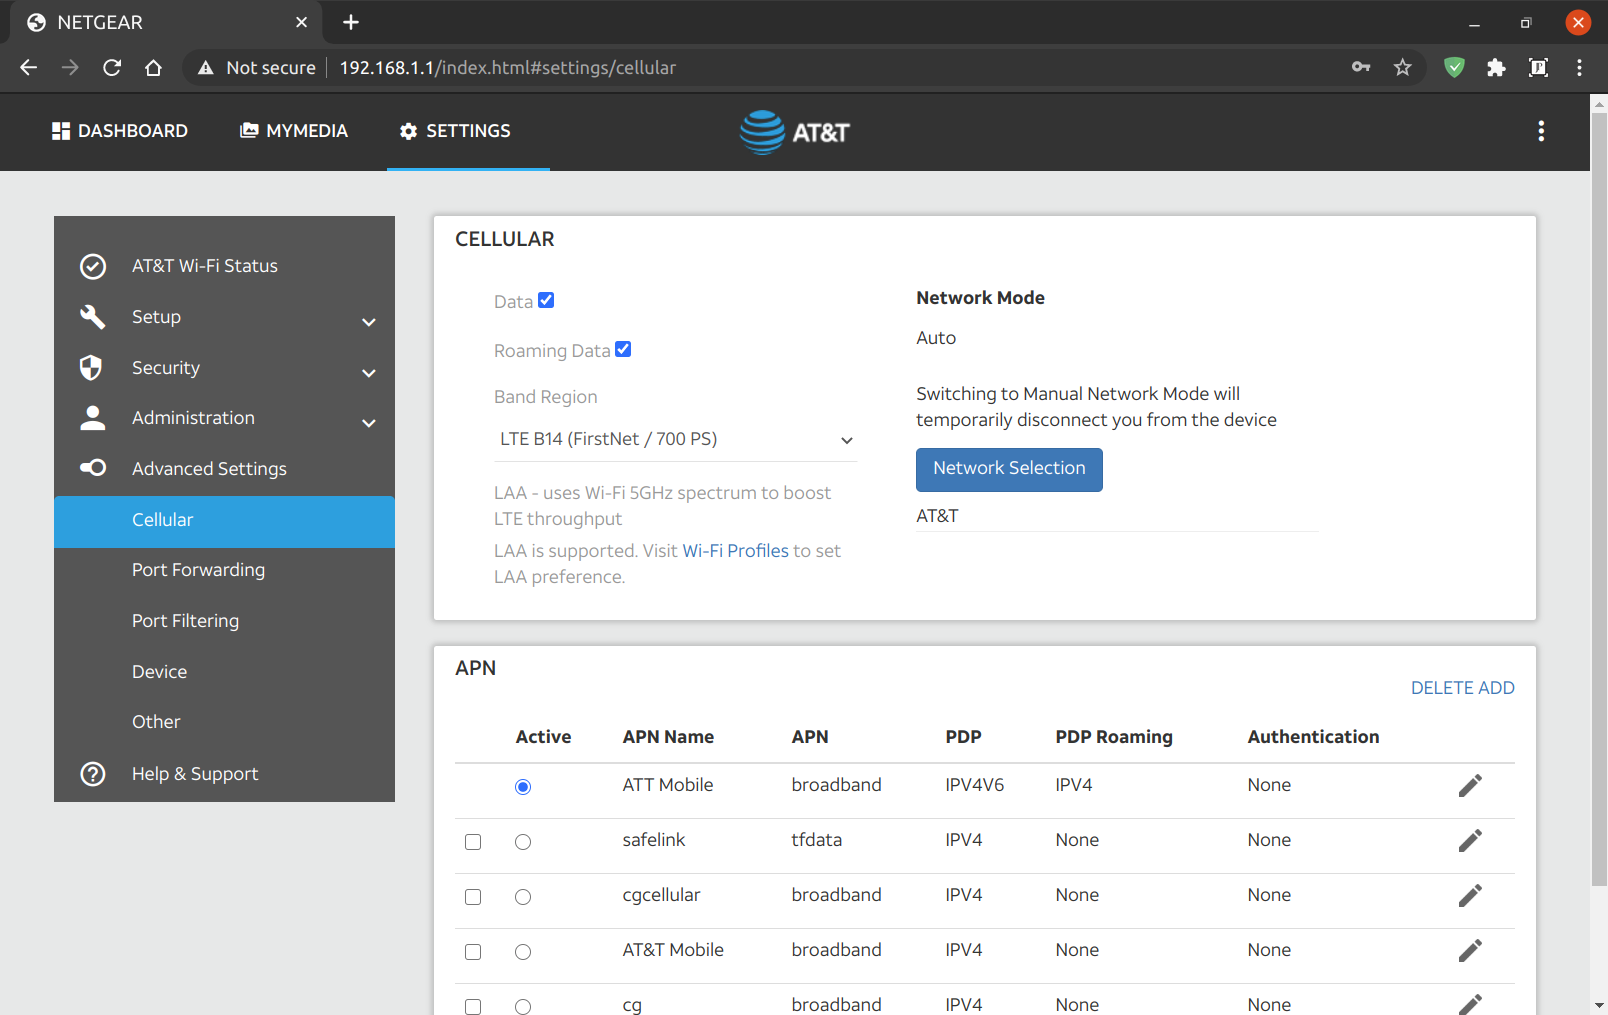
By plugging in the USB to my computer, and telnetting into the M1. I played around with the different LTE bands around my home, and various combinations using carrier aggregation.
#Open a terminal
telnet 192.168.1.1 5510
Edited the band selection dropdown:
AT!gstatus?
AT!band=?
AT!BAND=03,"LTE B2 (1900 MHz PCS)",           0,  2
AT!BAND=04,"LTE B4 (1700/2100 MHz AWS)",      0,  8
AT!BAND=05,"LTE B12 (700 MHz Lower B/C/A)",   0,  800
AT!BAND=06,"LTE B14 (FirstNet / 700 PS)",     0,  2000
AT!BAND=07,"LTE B30 (2300 MHz WCS)",          0,  20000000
AT!BAND=08,"LTE B66 (AWS-3)",                 0,  0,          2
AT!BAND=09,"LTE CA (B2+B4+B12+B14+B30)",      0,  2000280a
You need to reboot the router before the changes show up in the web gui.
I connected to each band individually, and ran a speed test. I then ran a speed test with all bands aggregated. Carrier aggregation with Band 14 doesn’t seem to work. Also, the builtin All LTE option doesn’t seem to choose Band 14. However, when I choose it manually, I get a great connection. Simply locking the device to use Band 14 gave me the best speeds.
LTE Band 14 with WiFi turned off sitting on my desk.

Much better than 0.768Mbps DSL, but not quite broadband.
I took it outside and set it facing the direction of the tower.

Sweet! Broadband Internet. I’ll make an enclosure for it, and run power and ethernet out to it.
I will order a pair of yagis. A type of directional antenna. For even faster speeds. FirstNet public safety LTE in the United States occupies two 10-MHz-wide blocks of spectrum at 758 MHz to 768 MHz (download), and at 788 MHz to 798 MHz (upload). So, I’ll be sure The antennas support those frequencies. The M1 has two external TS9 antenna ports.

Technical Specification
| Frequency Range | 698 – 894 MHz |
| Gain | 8dBi |
| Front to Back Ratio | bigger than 15dB |
| Impedance | 50 ohms |
| VSWR | Less than 1.5 |
| Cable Loss | 0.075 dB |
| Vertical Plane | 72°F ± 5°F |
| Horizontal Plane | 76°F ± 5°F |
| Polarization Type | Vertical or Horizontal |
| Connector Type | SMA Male |
| Number Of Element | 4 |
| Length without Cable | 37 cm |
| Weight | 0.7 Kg |
| Rated Wind Velocity | 150 Mile per Hour |
| Working temperature | -40°F ~ +140°F |
I had to order some SMA ends to shorten the antenna cable. You lose signal for every inch long your antenna cable is. I also ordered SMA to TS9 pigtails, and an outdoor enclosure.
I’ll set them up 90 degrees offset pointing at the same tower. I found my tower location using Opensignal app, then I used Google earth to find the heading. Which was for me 38 magnetic degrees from my house to the tower. I then used a compass app, or google maps to know where to point the antennas. I’m sure it will take some fine tuning. This is a great guide for doing line of sight with Google earth:
https://startyourownisp.com/posts/guide-to-google-earth/
{Speedtest}
There are three ways to use the M1 as a modem. You can connect via ethernet, USB, or WiFi. I found the best performance was wither USB or Ethernet with WiFi off.
#Check IMEI
ati#Restore corrupted IMEI
To unlock your NV:
https://github.com/bkerler/SierraWirelessGen
Installation
- Get python >=3.6 64-Bit~>
- git clone https://github.com/bkerler/edl/ ~>
- chmod +x edl/modem/sierrakeygen.py ~>
- cd edl/modem
- pip3 install -r requirements.txt
at!openlock?
./sierrakeygen.py -l <challenge> -d MDM9x40
AT!OPENLOCK="<generatedresponse>"
at!nvimeiunlock
#at!nvmeidunlock
at!nvencryptimei=xx,xx,xx,xx,xx,xx,xx,x0
#at!nvencryptmeid=xx,xx,xx,xx,xx,xx,xx
atiInstall and Configure WireGuard
From: https://www.stavros.io/posts/how-to-configure-wireguard/
Note: for the client configuration to work you must first have a working wireguard server.
#become root
sudo -i

#install wireguard
apt install wireguard

#create keys
cd /etc/wireguard
umask 077  # This makes sure credentials don't leak in a race condition.
wg genkey | tee privatekey | wg pubkey > publickey
#edit the config
nano -w wg0.conf
Client (Example config file) – wg0.conf
Add the client private key, the server public key, and the server IP address.
[Interface]
Address = 10.5.5.25
PrivateKey = client private key

#-------------DNS
#DNS = 10.5.5.1 #Server caching dnsmasq that forwards to azure in my case
#DNS = 168.63.129.16 #Azure
#DNS = 1.1.1.1 #Cloudflare
DNS = 176.103.130.130, 176.103.130.131 #AdGuard

#-------------MTU
MTU = 1280 #This may need to be changed depending on your connection to the internet.
#MTU = 1384
MTU = 1360

#-------------MSS Clamping
#PostUp = iptables -A FORWARD -p tcp --tcp-flags SYN,RST SYN -j TCPMSS --clamp-mss-to-pmtu
#PostDown = iptables -D FORWARD -p tcp --tcp-flags SYN,RST SYN -j TCPMSS --clamp-mss-to-pmtu


[Peer]
PublicKey = server public key
Endpoint = server IP address:51820
#AllowedIPs = 0.0.0.0/0 #Use this if you want all your traffic to pass through the VPN
AllowedIPs = 10.5.5.25/32

# This is for if you're behind a NAT and
# want the connection to be kept alive.
PersistentKeepalive = 25
Server (Example config file) – wg0.conf
Add the server private key, and each client’s public key.
[Interface]
Address = 10.5.5.1
PrivateKey =
ListenPort = 51820

[Peer]
PublicKey =
AllowedIPs = 10.5.5.5/32

[Peer]
PublicKey =
AllowedIPs = 10.5.5.25/32
Securing
After you’re done, run the following to make the directory and files readable only by administrators (it does contain secret keys, after all):
exit # exit rootsudo chown -R root:root /etc/wireguard/
sudo chmod -R og-rwx /etc/wireguard/*
Start and test wireguard
On both server, and client run:
sudo wg-quick up wg0; wg
#to bring it down
sudo wg-quick down wg0
Automatically run at startup
After you’ve created and secured the file, you can easily set WireGuard to initialize the VPN on startup if your OS is using systemd:
sudo systemctl enable [email protected]
Similarly, to start or stop the service:
sudo systemctl start [email protected]
sudo systemctl stop [email protected]
Android or iOS client
To turn your conf file into a qr code use:
qrencode -t ansiutf8 < wg0.confSet up DNS on the server
From: https://askubuntu.com/questions/1032450/how-to-add-dnsmasq-and-keep-systemd-resolved-18-04
Install openresolv on client
apt install openresolvInstall dnsmasq on server
apt install dnsmasq
nano -w /etc/dnsmasq.conf
server=168.63.129.16 #Azure
#server=176.103.130.130, 176.103.130.131 #Adguard
interface=lo
listen-address=10.5.5.1
bind-interfacesMake DNSMasq start after our wg-quick service:
systemctl edit dnsmasqpaste
[Unit]
[email protected]
[email protected]
Firewall on server
Allow udp port 51820 through your firewall in whatever cloud service you are using.
Allow Wireguard and DNS through local ufw firewall
ufw allow proto udp from any to any port 51820
ufw allow proto tcp from any to any port 53
From: https://ubuntu.com/server/docs/security-firewall
Make sure to edit the firewall policy’s in your cloud server’s management dashboard as well to allow port 52820. In my case, Azure.
sudo ufw status
Status: active

To                         Action      From
--                         ------      ----
22                         ALLOW       Anywhere
51820                      ALLOW       Anywhere
53                         ALLOW       Anywhere
/etc/default/ufw change the DEFAULT_FORWARD_POLICY to “ACCEPT”:
DEFAULT_FORWARD_POLICY="ACCEPT"
Then edit /etc/ufw/sysctl.conf and uncomment:
net/ipv4/ip_forward=1
Now add rules to the /etc/ufw/before.rules file. The default rules only configure the filter table, and to enable masquerading the nat table will need to be configured. Add the following to the top of the file just after the header comments:
# nat Table rules
*nat
:POSTROUTING ACCEPT [0:0]

# Forward traffic from eth1 through eth0.
-A POSTROUTING -s 10.5.5.0/24 -o eth0 -j MASQUERADE

# don't delete the 'COMMIT' line or these nat table rules won't be processed
COMMIT
sudo service ufw restartTest what is my ip, and dns leak
Gnome shell Indicator extension: https://extensions.gnome.org/extension/3160/wireguard-indicator/
Add a quicklaunch shortcut: https://blog.linuxserver.io/2019/11/24/connect-an-ubuntu-client-to-opnsense-wireguard-tunnel-with-a-gui-toggle-in-gnome/
]]>For the backgrounds to work you;ll need a solid color background. I ordered this green screen: https://amzn.to/2ZhoAkK.
I use Google meets, but this should work with any video conferencing software. (Google meets should be rolling out virtual backgrounds, and blurring in the coming months.) From: https://cloud.google.com/blog/products/g-suite/introducing-some-new-meet-features
Install OBS
sudo snap install obs-studioInstall V4L2
sudo apt install v4l2loopback-dkmsCreate dummy video device, and make is persist across reboots.
create the config file:
nano -w /etc/modules-load.d/obscam.confAdd the below contents:
v4l2loopback devices=1 video_nr=10 card_label="OBS Cam" exclusive_caps=1Next time you reboot the module should be automatically loaded. Manually add the module with the currently running system:
sudo modprobe v4l2loopback devices=1 video_nr=10 card_label="OBS Cam" exclusive_caps=1OBS Plugin obs-v4l2sink
NOTE: This step is no longer necessary in modern version of OBS. As it is now a base feature. You may need to restart OBS to see the new “Start Virtual Cam” button to appear.
You may have to install libobs, and libobs-dev
sudo apt install libobs libobs-devDownload and Compile OBS plugin obs-v4l2sink
sudo apt install qtbase5-dev
git clone --recursive https://github.com/obsproject/obs-studio.git
git clone https://github.com/CatxFish/obs-v4l2sink.git
cd obs-v4l2sink
mkdir build && cd build
cmake -DLIBOBS_INCLUDE_DIR="../../obs-studio/libobs" -DCMAKE_INSTALL_PREFIX=/usr ..
make -j4
sudo make install
Now start OBS Studio and configure the V4L2 video output to /dev/video10 via the new menu item “Tools”->”V4L2 Video Output”:

Add a Chromakey filter.
Here is a good guide: https://gamingcareers.com/guides/green-screen-in-obs-slobs/
Add border, presets, LUTs, transitions, etc…
Add scenes like thank you, thumbs up, screen sharing, other camera angles etc…
Using Google Meet with the Virtual Camera
Start a Google Meet via https://meet.google.com/ and go to settings:

More Reading
Pretty cool virtual background way from scratch: https://elder.dev/posts/open-source-virtual-background/
Another cool virtual background: https://github.com/floe/deepbacksub
I’m also testing Webcamoid: https://webcamoid.github.io/. (Seems to crash quite a bit.)
]]>Parsec is the only option that allows you to play ANY Windows game. You can then stream Geforce Now, Google Stadia, Steam, Epic Games, Origins, and any other standalone windows game. You can also use it as performant remote desktop for CAD or other graphics heavy programs.
It allows you to reduce the framerate to 30fps, the resolution to 1280×720, and the bitrate to 1Mbps. Even though I have “3Mbps” DSL, in the real word it’s more like 2.5Mbps. When I set the bitrate to 2Mbps it saturates my bandwidth sometimes. I found the best was to set bitrate to 1Mbps or 2Mbps depending on the time of day, or if there was anyone else using it.
Create your cloud virtual machine in Azure, and install parsec
From: https://medium.com/azure-cloud/a-killer-guide-for-cloud-gaming-on-azure-march-2020-1aa56d13fba3
- Connecting to the VM with TeamViewer, open a prompt as admin (Start Menu -> search for “cmd” -> right click on command prompt and select Run as Administrator).
- Go to the C:\Program Files\NVIDIA Corporation\NVSMI folder, and run nvidia-smi. This will get you a table that gives you both what mode your Tesla is set to (which will be TCC by default, check under the heading TCC/WDDM), and the GPU_ID, which is the thing under the Bus-Id heading.
- Run nvidia-smi -g {GPU_ID} -dm {0|1} with your Bus-Id and 0 to set it to WDDM, like so (the GPU_ID may differ):
nvidia-smi -g 1:00:00.0 -dm 0
Instead of Teamviewer you can use the open source DWService: https://www.dwservice.net/
If using a different cloud provider, check out:
https://github.com/parsec-cloud/Parsec-Cloud-Preparation-Tool
My parsec config:
# All configuration settings must appear on a new line.
# All whitespace, besides the newline character '\n', is ignored.
# All settings passed via the command line take precedence.
# The configuration file will be overwritten by Parsec when changing settings,
#   so if you edit this file while Parsec is running, make sure to save this file
#   and restart Parsec immediately so your changes are preserved.

# Example:
# encoder_bitrate = 10

app_run_level = 3
app_discord = 0
client_vsync = 0
client_decoder_index = 2
client_decoder_h265 = true
server_resolution_x = 1280
server_resolution_y = 720
encoder_bitrate = 2
encoder_fps = 30
encoder_fps_1 = 30
I installed parsec from: https://parsecgaming.com/downloads/
I use Ubuntu 20.04 and and Nvidia Geforce 1050ti video card. I had to install this tweak to get Parsec to do hardware decoding using libva-vdpau vaapi. I borrowed it from the moonlight project snap.
I got this error when running vainfo to verify the VAAPI-VDPAU wrapper.
vainfo
error: XDG_RUNTIME_DIR not set in the environment.
libva info: VA-API version 1.7.0
libva info: Trying to open /usr/lib/x86_64-linux-gnu/dri/nvidia_drv_video.so
libva info: va_openDriver() returns -1
vaInitialize failed with error code -1 (unknown libva error),exit
My solution was to borrow nvidia_drv_video.so from moonlight, I have not idea why this was not installed with the proprietor nvidia drivers.
sudo snap install moonlight
sudo ln -s /snap/moonlight/current/usr/lib/x86_64-linux-gnu/dri/nvidia_drv_video.so /usr/lib/x86_64-linux-gnu/dri/nvidia_drv_video.so
It used to be part of the vdpau-va-driver package, but that is no longer available on 20.04. It’s replaced by the mesa-va-driver, which does not contain it.
Parsec Shortcuts
From: https://support.parsecgaming.com/hc/en-us/articles/115003632451-Parsec-Shortcuts
CLIENT MENU OPTIONS
- Interact with chat – ctrl + shift + c
- Toggle menu – ctrl + shift + m
- Toggle windowed mode – ctrl + shift + w
- Detach mouse – ctrl + alt + z
- Immersive mode – ctrl + shift + i
EXITING THE STREAM
- Quitting the Mac Application – command + Q or command + W
- Quitting the Windows Application – alt + F4
- Quitting the Raspberry Pi Application – ctrl + alt + ~
- Quitting the Linux Application – ctrl + alt + ~
FRIEND SHORTCUTS
- Allowing access to a friend trying to make a connection who doesn’t have admin access – ctrl + F1 when they try to connect
- Kick everyone from the stream all at once (the panic button!) – ctrl + F3
IMMERSIVE MODE
- Toggling the Windows hotkey passthroughs – ctrl + shift + i
- This allows you to send data to the host when you use ctrl + alt + delete, the Windows button, alt + tab
Good too: https://github.com/mcblum/ddclient-cloudflare-ubuntu
Prepare
- Create the subdomain in Cloudflare, and set to DNS only. Unless you are hosting a website at that subdomain.
- Grab your Global API found under “My profile –> API tokens”
- On the server install ddclient.
sudo apt install ddclient libdata-validate-ip-perlGrab the latest version (No longer needed in 22.04)
wget https://github.com/ddclient/ddclient/archive/v3.9.1.tar.gz
tar -xf v3.9.1.tar.gz
sudo cp ddclient-3.9.1/ddclient /usr/sbin/ddclient
rm -rf v3.9.1.tar.gz ddclient-3.9.1/
sudo mkdir /etc/ddclient
sudo mv /etc/ddclient.conf /etc/ddclient/
Configuration
sudo nano -w /etc/ddclient.conf
# Configuration file for ddclient generated by debconf
#
# /etc/ddclient.conf
# Configuration file for ddclient

##
## Global Config
##
daemon=500
ssl=yes

##
## sub.domain.tld - Cloudflare ## Update Me
##
protocol=cloudflare
use=web
[email protected] ## Update Me with cloudflare login email
password=abcredactedxyz ## Update Me with cloudflare Global API found under "My profile --> API tokens"
zone=domain.tld ## Update Me with the domain
sub.domain.tld ## Update Me with the subdomain
To test:
sudo ddclient -query
sudo ddclient -daemon=0 -verbose -noquiet
sudo service ddclient statusCalifornia Teleconnect Fund (CTF)
The CTF program provides a 25% off voice services and a 50% discount for broadband on select communications services to schools, libraries, hospitals and other non-profit organizations.
The program was established by Decision 96-10-066 on October 25, 1996. In this decision, the California Public Utilities Commission reaffirmed its commitment to universal service, and created the CTF program in accordance with state and federal directives. The program is funded through a surcharge on all customers that purchase intrastate telecommunications services.
Eligible types of nonprofits:
- CTF Application Form for Schools
- CTF Application Form for Libraries
- CTF Application Form for Government Hospitals and Clinics
- CTF Application Form for Community Colleges
- CTF Application Form for Community-Based Organizations (and Healthcare CBO and 2-1-1 Providers)
- Select the service(s) provided to the community.
- 2-1-1 Service Provider
- Job Placement / Training
- Computer Technology Program
- Educational Instruction
- Healthcare
More info here: http://www.cpuc.ca.gov/ctf/
Onced approved, if you have Comcast, you’ll want to send an email to [email protected]. Please make sure to include your account number, CTF approval number, and a PDF copy of your CTF approval letter.
]]>As you can see from the matrix below there are MANY ways of providing desktops to your users.
However, I think this way has many advantages for a Nonprofit. I would recommend it generally, although of course other topographies are more useful in specific situations.
Benefits for a Nonprofit
- Green computing – Thin clients use less power than traditional workstations.
- Reduced maintenance costs – Thin client deployment means you’re only maintaining a couple servers, instead of multiple traditional workstations. Using Azure cloud means you don’t have to maintain server hardware.
- 100% free horizontal software – Completely free Open Source horizontal market software.
- Discounted vertical market software – Purchase heavily discounted MS remote desktop licenses at Techsoup. Along with anything else you might need. e.g. Quickbooks, MS Office, and any other vertical market software. https://www.techsoup.org/
- $3500 Azure Credit, Free Office 360 – Free cloud servers, Office.
Apply for Microsoft Nonprofit here: https://nonprofit.microsoft.com/register - Free Voice,Gsuite,etc.. – Free cloud Telephony, calendaring, file management, and email with custom domain.
Apply for Google Nonprofit here: https://www.google.com/nonprofits/ - Free hardware; Nevada County among others will donate their old computers, and peripherals to any eligible local nonprofit. Perfect for blazingly fast thin clients. Bring your tax exempt paperwork to the warehouse on the last Friday of the month. Or, try Purchasing hardware from your local government entity here: https://www.publicsurplus.com/sms/nevadacounty,ca/list/current?orgid=315996 After that try eBay: https://rover.ebay.com/rover/1/711-53200-19255-0/1?mpre=https%3A%2F%2Fwww.ebay.com%2Fb%2FPC-Desktops-All-In-One-Computers%2F179%2Fbn_661752&campid=5337848787&toolid=20008
- No taxes – If you use Comcast as your internet provider, make sure to file tax exemption paperwork with them to waive the applicable taxes. Email tax exempt certificate to: [email protected] . Include service address & account #.
- 50% off internet – If you are school, or other eligible nonprofit in California sign up here for 50% off your internet bill. https://jphein.com/discounted-phone-and-internet-for-nonprofits-in-california/
Terms
- [wiki]Vertical market software[/wiki] – https://en.wikipedia.org/wiki/Vertical_market_software
- [wiki]Thin client[/wiki] – https://en.wikipedia.org/wiki/Thin_client
- [wiki]Linux Terminal Server Project[/wiki] (LTSP) – https://en.wikipedia.org/wiki/Linux_Terminal_Server_Project
- [wiki]Ubuntu[/wiki] – https://en.wikipedia.org/wiki/Ubuntu
- [wiki]Remote Desktop[/wiki]
Guide
Follow along. At the end of this guide you should be able to plug in any number of old computers without hard drives into your local network. Then have them boot blazingly fast Windows based modern software. Wireless, and remote VPN clients are also supported.
In this setup all thin clients will be sharing a single Windows 2016 Datacenter instance. However, you can provide any number of environments using this method, including huge VDI deployments. My favorite is using LTSP Ubuntu fat client desktops with RemoteApps for seamless cloud integration of necessary windows based proprietary software.
I am using Ubuntu 18.04 Bionic Beaver for the LTSP server, because LTSP does not currently work with Ubuntu 18.10 Cosmic Cuttlefish.* In my case the entire setup was virtualized in the Azure cloud using KVM Virtual Machine Manager for virtual thin clients.
It might look like this:
[Azure Standard D4s v3[[PXE thin client – KVM guest] –> [Ubuntu 18.04] LTSP Server]] –>[Azure Standard NV6 [Windows 2016]]
In real life the more likely scenario would be to install Ubuntu on a bare metal server onsite. Then, install Ubuntu 18.04 inside a KVM vm. Plug a thin client into your network, and configure it for PXE boot in BIOS. It would look a little like this:
[PXE thin client] –> [[Ubuntu 18.10] [Ubuntu 18.04 KVM guest LTSP server]] –> [Firewall] –> [Internet] –> [Azure Standard NV6 [Windows 2016]]
In this guide I will be first showing you how to set up the virtualized system, and then go into some changes you’ll need to make in the field.
Requirements
- An internet connection. 3MB/s or more recommended.
- A computer with keyboard and display capable of running at least SSH. To issue the commands from.
- A computer capable of running Ubuntu with at least one network card. Or a virtual machine capable of nested virtualization like the Azure Standard D4s v3. For the LTSP server.
- A virtual or real windows machine locally or in the cloud. You’ll need Remote desktop licenses if you want to use microphone forwarding. If using Azure, not every region has the NVIDIA Tesla servers (NV6) for hardware graphics rendering. USA South Central is what I used. This is used for the desktop environment.
IPs
- 10.0.0.1 – Gateway.
- 10.0.0.5 – eth0 – Local interface on Ubuntu server – Connected to the Internet.
- 192.168.122.1 – virbr0 – Virtual bridge on Ubuntu server for testing virtual thin clients.
- 10.0.0.4 – Windows 2016 datacenter RDP server with NV6 Nvidia Tesla hardware.
Create your Azure Virtual Machines
After signing up and being accepted to Microsoft Nonprofit, verify your $3500 credit here: https://www.microsoftazuresponsorships.com/Balance
Create your virtual machines here: https://portal.azure.com
Note: DO NO USE accelerated networking on the Ubuntu Server.
LTSP Server
- Image type: Ubuntu 18.04
- Size: Azure Standard D4s v3
Desktop Server
- Image type: Windows 2016 Datacenter
- Size: Azure Standard NV6
[jbox]Azure comes with a premade Ubuntu 18.04 image, but if you are doing this in the field you would need to install Ubuntu on your server:
Install Ubuntu 18.04.1 Desktop (Minimal)
- Ubuntu 18.04.1 Desktop.
- Download ISO here: https://www.ubuntu.com/download/desktop
- Install the desktop version, minimal install.
- Instructions here: https://jphein.com/how-to-install-ubuntu-18-04-18-10-to-an-usb-3-1-m-2-16gb-drive-using-kvm/
If you decide to have a local Windows server instead or in addition to the Azure vm, you’ll need to install Windows locally.
Install Windows 2016 Datacenter
- Download ISO from Microsoft Volume Licensing Center
- Install
[/jbox]
Configure Windows 2016 Datacenter
Configure remote desktop for microphone redirection:
- Install Remote Desktop Session Host
- You’re either still inside the grace period OR have the Remote Desktop Licensing role installed and a valid CAL
- Make sure the remote desktop group policy allows audio recording
Configure graphics acceleration: https://lg.io/2016/10/12/cloudy-gamer-playing-overwatch-on-azures-new-monster-gpu-instances.html
Configure the Ubuntu and install LTSP Server
[jbox]You can find a bash script automating all the below commands here: https://raw.githubusercontent.com/jphein/boxen/master/boxenbrain [/jbox]
To manually install BoXenLinux we will be configuring LTPS using the Chrootless Proxy mode for in the field. It is the easiest of the 4 ways to install LTSP. However, for the Azure cloud we’ll need to install using a chroot.
[jbox color=green]Set a static IP for your wired network interface in the field
Microsoft azure VM comes with the static IP set on your default interface. However, in the field you’ll need to set a static IP address.
https://www.itzgeek.com/how-tos/linux/ubuntu-how-tos/netplan-how-to-configure-static-ip-address-in-ubuntu-18-04-using-netplan.html
https://netplan.io/examples
[/jbox]
Optional: Install OpenSSH server
If using the Azure install as the LTSP server, you’ll want to overwrite the existing sshd_config so that you can using password login if you used a key when creating the VM.
sudo apt install ssh
Install LTSP and epoptes (epoptes lets you remote desktop in and help anyone using a thin client), Instructions from http://wiki.ltsp.org/wiki/Installation/Ubuntu:
sudo add-apt-repository --yes ppa:ts.sch.gr #The Greek Schools repository
sudo apt install --yes --install-recommends ltsp-server-standalone ltsp-client epoptes
Configure dnsmasq
Note: You may want to edit the /etc/dnmasq.d/ ltsp-server-dnsmasq.conf and add “dhcp-option=3,192.168.122.1” to set a different gateway, but probably not.
sudo ltsp-config dnsmasq --enable-dns
sudo service dnsmasq restart
Add yourself the epoptes group
sudo gpasswd -a ${SUDO_USER:-$USER} epoptes
Was told to remove these packages
sudo apt purge --yes --auto-remove mate-hud snapd
[jbox color=blue title=”Optional: Chroot Install”]
Build a chroot client for alternate arch, dekstop enviroment or package base
Grab freerdp’s key
cd /etc/ltsp
sudo wget http://pub.freerdp.com/repositories/ADD6BF6D97CE5D8D.asc
- Option 1 – with command
sudo ltsp-build-client --purge-chroot --mount-package-cache --mirror 'http://azure.archive.ubuntu.com/ubuntu/'
 --apt-keys '/etc/ltsp/ADD6BF6D97CE5D8D.asc, /etc/apt/trusted.gpg.d/ts_sch_gr_ubuntu_ppa.gpg'
 --extra-mirror 'http://ppa.launchpad.net/ts.sch.gr/ppa/ubuntu bionic main, http://pub.freerdp.com/repositories/deb/bionic/ freerdp-nightly main'
 --late-packages epoptes-client freerdp-nightly --prompt-rootpass --fatclient
- OR, Option 2 – using my ltsp-build-client.conf
sudo wget https://github.com/jphein/boxen/raw/master/etc/ltsp/ltsp-build-client.conf
sudo ltsp-build-client --config ltsp-build-client.conf
You may want to install a new kernel like this one if the azure kernel doesn’t work with all of KVM’s input drivers:
sudo apt-get install linux-image-lowlatency
Then you have to edit the update-kernels.conf file, so that LTSP chooses that one to boot the client.
Create some symlinks so freerdp-nightly is more easy t my lazy scripting
sudo ltsp-chroot
ln -s /opt/freerdp-nightly/bin/xfreerdp /usr/bin/xfreerdp-nightly
ln -s /usr/share/ltsp/screen.d/xfreerdp /usr/share/ltsp/screen.d/xfreerdp-nightly
exit
Create GUI login screen for xfreerdp-nightly (Not updated!)
cd /opt/ltsp/amd64/usr/share/ltsp/screen.d/

sudo wget https://raw.githubusercontent.com/jphein/boxen/master/rdpgui

sudo wget https://raw.githubusercontent.com/jphein/boxen/master/xfreerdp-prompt

sudo chmod +x rdpgui xfreerdp-prompt
sudo ltsp-update-image
Note: You may get this error on Microsoft Azure VM! https://bugs.launchpad.net/ubuntu/+source/ltsp/+bug/1802707 hmmmm…. This script seems to fix it:
#!/bin/bash
# tadaen sylvermane | jason gibson
# configure locales for ubuntu bionic ltsp chroot creation


for var in LC_ALL= LANG= ; do
        export "$var"en_US.UTF-8
done
ltsp-build-client --chroot "$1"
[/jbox]
[jbox color=green title=”Local Chrootless Install”]
This is the recommended, and simplest install
Install FreeRDP-nightly and client zenity GUI
sudo sh -c 'echo "deb http://pub.freerdp.com/repositories/deb/$(lsb_release -cs)/ freerdp-nightly main" >> /etc/apt/sources.list.d/freerdp-nightly.list'
wget -O - http://pub.freerdp.com/repositories/ADD6BF6D97CE5D8D.asc | sudo apt-key add -
sudo apt update
sudo apt install --yes freerdp-nightly
sudo ln -s /opt/freerdp-nightly/bin/xfreerdp /usr/bin/xfreerdp-nightly
cd /usr/share/ltsp/screen.d/
sudo ln -s xfreerdp xfreerdp-nightly
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/usr/share/ltsp/screen.d/rdpgui
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/usr/share/ltsp/screen.d/xfreerdp-prompt
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/usr/share/ltsp/screen.d/launch
sudo mkdir boxen
cd boxen
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/usr/share/ltsp/screen.d/boxen/welcome
cd ..
sudo ln -s launch welcome
sudo ln -s /sbin/shutdown shutdown
sudo chmod +x rdpgui xfreerdp-prompt launch boxen/welcome
Create LTSP client NBD image using the chrootless method of the servers root /
You need to run this any time you make changes to your filesystem you want to be updated in your LTSP client.
sudo ltsp-update-image --cleanup /
[/jbox]
Grab the lts.conf for our thin clients
cd /var/lib/tftpboot/ltsp/amd64/
sudo wget https://raw.githubusercontent.com/jphein/boxen/master/var/lib/tftpboot/amd64/lts.conf
Edit lts.conf to suit your needs
nano -w lts.conf
Test with KVM virtual pxe thin client
If you are already using KVM to install Ubuntu in a VM then you don’t need to install it again. However, if you are using a real bare metal server then you’ll need to run the install command.
sudo apt install virt-manager
[jbox]Libvirtd will run dnsmasq on virbr0 by default. We need to kill that instance and restart the global dnsmasq with our LTSP configs. You will need to killall and restart dnsmasq every time you reboot.
###dnsmasq hack for testing
sudo mv /etc/dnsmasq.d/libvirt-daemon /root/
sudo sh -c 'echo "dhcp-range=192.168.122.20,192.168.122.250,8h" >> /etc/dnsmasq.d/ltsp-server-dnsmasq.conf
#These steps will need to performed again if you reboot
sudo killall dnsmasq
sudo service dnsmasq restart
[/jbox]
#Create the PXE test KVM client
sudo virt-install
  --name pxe
  --memory 4096
  --vcpus 2
  --disk none
  --pxe
  --os-variant ubuntu17.10
  --wait 0
Connect locally using very nice spice
virt-viewer --connect qemu:///system pxe
Connect remotely using spice
virt-viewer --connect qemu+ssh://[email protected]/system pxe


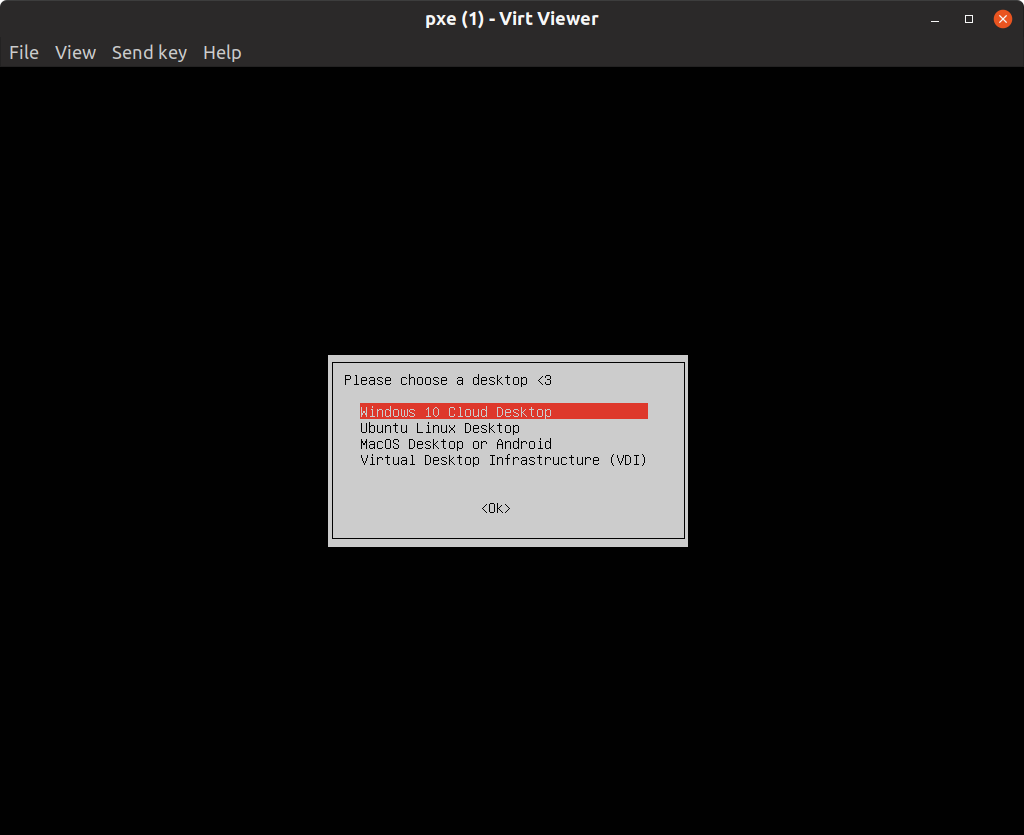
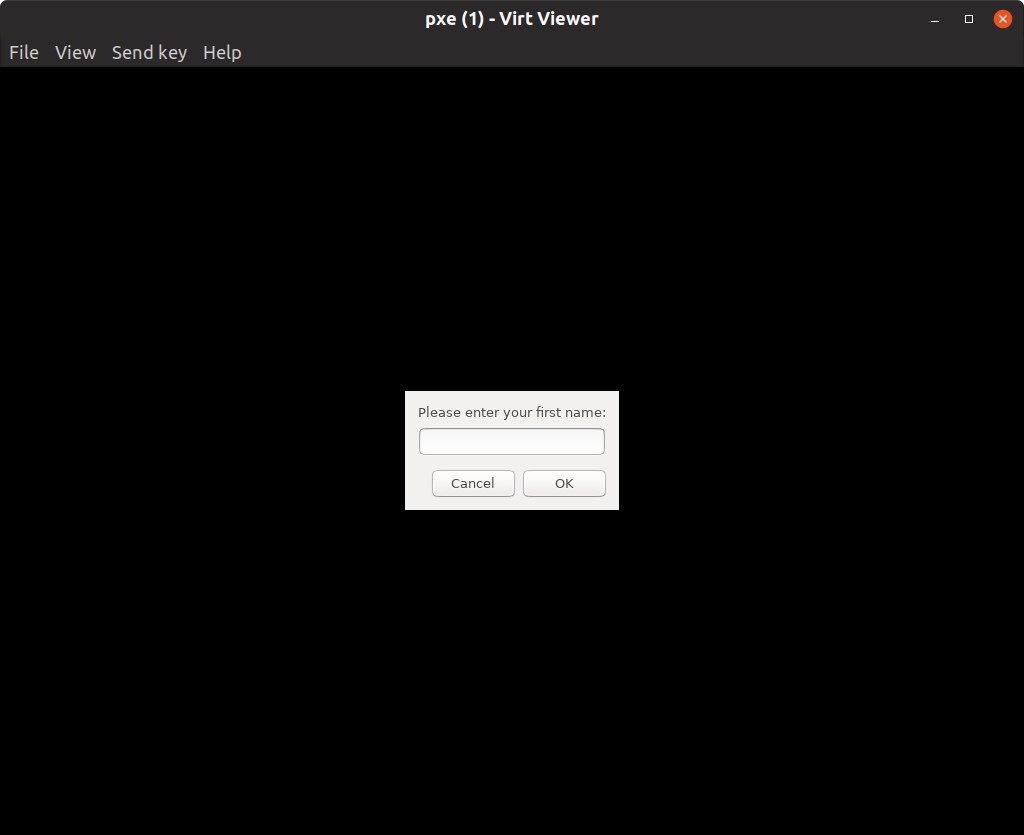
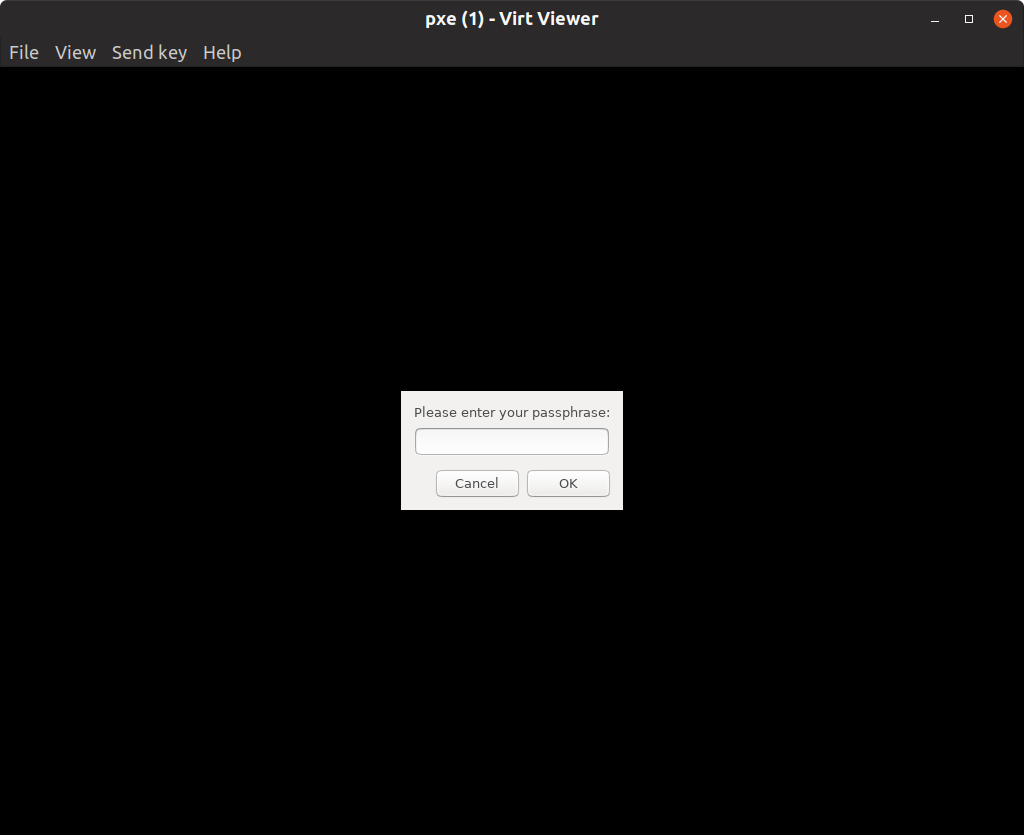
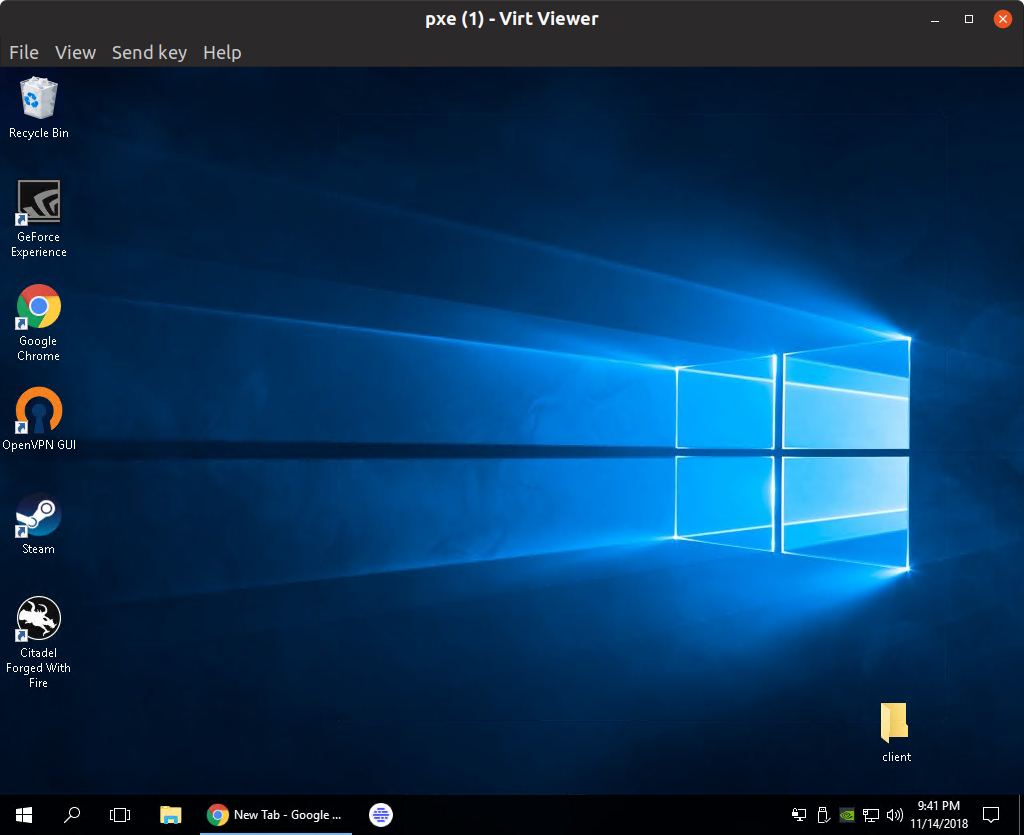 Tada!!!
See also
lts.conf manpage ltsp-build-client manpage ltsp-update-image manpage ltsp-config manpage ltsp-chroot manpage http://wiki.ltsp.org/wiki/Installation/Ubuntu https://help.ubuntu.com/community/HowToSetupLTSPDevelEnvironment https://github.com/wyllianbs/xfreerdp-gui https://unix.stackexchange.com/questions/119880/make-freerdp-prompt-user-for-username-and-password/187370 http://www.saminiir.com/debugging-pxe-boot/
* Ubuntu 18.10 I previously tried this with Ubuntu 18.10 Cosmic Cuttlefish, and ran into some issues. Mainly the maintainer of LTSP for Ubuntu does not fix anything that is not a LTS release.
Optional Install ltsp-manager
sudo add-apt-repository --yes ppa:franz-die/ltsp-manager; apt update

sudo apt install ltsp-manager
Optional: Install X2Go remote desktop software
sudo add-apt-repository ppa:x2go/stable
sudo apt-get update
sudo apt-get install x2goserver x2goserver-xsessions x2gomatebindings
Optional: Install Ubiquity to install Ubuntu on PXE booted clients or servers
sudo apt-get install ubiquity ubiquity-frontend-gtk
Running it is a manner of running from the client
ubiquity gtk_ui
Optional: Add iPXE to grub menu
apt install grub-ipxe
[jbox]Optional: Set up Firewall with IP Masquerading
Probably won’t need to do this.
First, packet forwarding needs to be enabled in ufw. Two configuration files will need to be adjusted, in /etc/default/ufw change the DEFAULT_FORWARD_POLICY to “ACCEPT”:
sudo nano -w /etc/default/ufw #change DEFAULT_FORWARD_POLICY="ACCEPT"
Then edit /etc/ufw/sysctl.conf,
sudo nano -w /etc/ufw/sysctl.conf
and uncomment:
net/ipv4/ip_forward=1
net/ipv6/conf/default/forwarding=1
Now add rules to the /etc/ufw/before.rules file. The default rules only configure the filter table, and to enable masquerading the nat table will need to be configured. Add the following to the top of the file just after the header comments:
sudo nano /etc/ufw/before.rules
# nat Table rules
*nat
:POSTROUTING ACCEPT [0:0]
# Forward traffic from eth1 through eth0.
-A POSTROUTING -s 192.168.122.0/24 -o eth0 -j MASQUERADE
# don’t delete the ‘COMMIT’ line or these nat table rules won’t be processed
COMMIT
Allow SSH
sudo ufw allow 22
sudo ufw allow from 192.168.122.0/24
sudo ufw enable
[jbox]
Optional: Install apt-cacher
apt-cacher will cache packages so you don’t waste your time downloading them again again.
sudo apt install apt-cacher
sudo nano /etc/apt-cacher/apt-cacher.conf #Uncomment allowed_hosts= *
sudo ufw allow 3142/tcp
sudo sh -c 'echo "Acquire::http::Proxy "http://10.0.0.5:3142"";' > /etc/apt/apt.conf.d/01proxy
sudo /usr/share/apt-cacher/apt-cacher-import.pl -l /var/cache/apt/archives
sudo service apt-cacher restart
Optional: Test with QEMU
Set up virtual bridge for client networking
On the azure VM I was able to use the default virtual bridge virbr0. Just commented out the dnsmasq.d/ file libvirt that prevented dnsmasq from serving IPs on that network. However, testing on a real server I needed to make my own bridge. These commands should not be issued if working on your server remotely. Only a local bare metal install should issue these commands.
sudo ip tuntap add dev virttap mode tap user $USER
sudo brctl addbr virtbr
sudo brctl addif virtbr eth0 # your LAN interface
sudo brctl addif virtbr virttap
sudo ip link set virtbr up
sudo ip link set eth0 up
sudo ip link set virttap up
dhclient virtbr
You may need to restart dnsmasq again
sudo service dnsmasq restart
Run QEMU to test your LTSP setup
cd
qemu-img create -f vmdk testpxe.vmdk 10
/usr/bin/qemu-system-x86_64 -m 1024 -hda testpxe.vmdk
                              -boot n
                              -option-rom /usr/share/qemu/pxe-rtl8139.rom
                              -net nic
                              -net tap,ifname=virttap,script=no,downscript=no
]]>